ToolMage
Sign in

Best 1 Cybersecurity AI tools for Learning

Popular Cybersecurity AI tools in Learning include TripleTen, helping you work more efficiently.

TripleTen

TripleTen

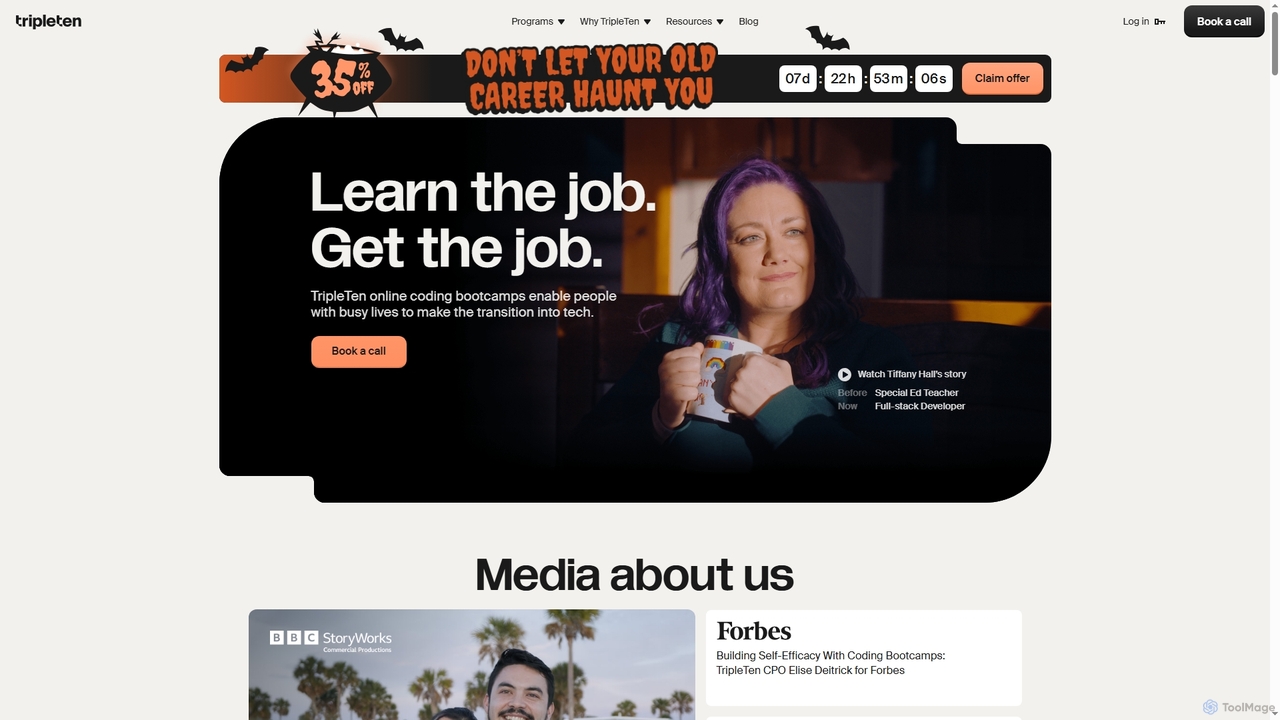
TripleTen offers online, part-time coding bootcamps designed to equip individuals with in-demand tech skills for career transformation. Specializing in fields like Software Engineering, AI & Machine Learning, QA Engineering, BI Analytics, Cyber Security, and UX/UI Design, TripleTen provides structured curricula aimed at preparing students for successful roles in the technology industry.

Tech Training
Visits 1.6MFavorites 144Likes 158

About Cybersecurity

AI Cybersecurity tools are a class of solutions that leverage machine learning to proactively detect, predict, and respond to digital threats. These tools analyze vast datasets of network traffic, user behavior, and threat intelligence to identify anomalies and patterns that traditional rule-based systems miss. This enables security teams to automate threat hunting, accelerate incident response, and learn from evolving attack vectors, significantly strengthening an organization's security posture. They represent a critical evolution in the learning and adaptation process of modern defense systems.

Core Features

  • Threat Detection & Prediction: Uses machine learning models to identify both known malware and novel, zero-day attacks in real-time.
  • Behavioral Analytics (UEBA): Establishes baseline user and entity behavior to detect insider threats, compromised accounts, or lateral movement.
  • Automated Incident Response (SOAR): Automates security workflows, such as quarantining infected devices or blocking malicious IPs, to accelerate containment.
  • AI-Powered Vulnerability Management: Scans systems for weaknesses and uses AI to prioritize patching based on exploitability and potential impact.
  • Advanced Phishing Detection: Analyzes email content, sender reputation, and URL structure with deep learning to block sophisticated phishing attempts.

Use Cases

These tools are essential for Security Operations Centers (SOCs), IT security analysts, and compliance officers in data-sensitive industries like finance, healthcare, and e-commerce. They are applied to monitor cloud infrastructure (AWS, Azure), secure endpoints and IoT devices, and perform large-scale analysis of security logs to uncover hidden threats.

How to Choose

When selecting an AI Cybersecurity tool, evaluate its integration capabilities with your existing security stack (e.g., SIEM, firewalls). Assess the sophistication of its machine learning models and its documented false positive rate. Consider the extent of its automation features for incident response and the clarity of its analytics dashboards for effective decision-making.

Cybersecurity use cases

1

Automated Threat Hunting in a SOC

A Security Operations Center (SOC) analyst is tasked with monitoring a massive corporate network that generates millions of security logs per hour. Manually sifting through this data is impossible. By using an AI Cybersecurity platform, the system continuously analyzes all data streams in real-time. The AI flags a subtle, low-and-slow data exfiltration pattern across multiple servers that would be invisible to human analysts. It automatically correlates these events, assigns a high-risk score, and generates an alert with a full attack timeline, allowing the analyst to immediately contain the breach, saving potentially millions in damages.

2

AI-Powered Phishing Campaign Detection

An IT administrator for a large corporation needs to protect thousands of employees from sophisticated spear-phishing attacks. Traditional filters often miss emails that don't contain obvious malicious links or attachments. They deploy an AI email security tool that analyzes not just keywords, but also the linguistic style, sender reputation, and contextual relationships within the email. The AI detects a campaign targeting executives with emails that impersonate a trusted vendor. It identifies the subtle change in tone and unusual request, blocking all related emails across the organization before any user clicks the link, thus preventing a major security incident.

3

Insider Threat Detection with UEBA

A financial institution is concerned about data theft from internal employees. They implement a User and Entity Behavior Analytics (UEBA) tool. The AI spends a few weeks learning the normal data access patterns for every employee and system. Later, it detects an anomaly: an accountant, who normally only accesses financial records during business hours, begins downloading large volumes of client data late at night from a personal device. The system immediately flags this as high-risk behavior and alerts the security team, who can investigate and intervene before sensitive information leaves the company.

4

Prioritizing Vulnerability Remediation

A DevOps team runs a weekly scan that identifies hundreds of new vulnerabilities across their cloud applications. It's impossible to patch everything at once. They use an AI-powered vulnerability management tool that goes beyond simple CVSS scores. The AI analyzes threat intelligence feeds, exploit availability in the wild, and the asset's business criticality. It then generates a prioritized list, highlighting the top 10 vulnerabilities that pose the most immediate and significant risk. This allows the team to focus their limited resources on fixing the most critical issues first, drastically reducing their attack surface with maximum efficiency.

5

Securing Cloud Infrastructure in Real-Time

A cloud security engineer is responsible for a complex multi-cloud environment (AWS and Azure). Manually tracking configurations, permissions, and network traffic for security risks is a constant challenge. They deploy an AI-powered Cloud Security Posture Management (CSPM) tool. The tool continuously scans the environment, using machine learning to detect risky misconfigurations, anomalous API calls, and potential intrusions that deviate from learned normal behavior. When it detects a publicly exposed storage bucket containing sensitive data, it sends an immediate, high-priority alert, enabling the engineer to remediate the issue in minutes instead of days, preventing a potential data breach.

6

Accelerating Malware Analysis and Reverse Engineering

A cybersecurity researcher receives a new, unknown malware sample. Manually reverse-engineering it could take days or weeks. Instead, they submit the sample to an AI-powered sandbox. The AI automatically executes the malware in a secure, isolated environment. It observes the malware's behavior, such as network connections, file modifications, and registry changes. The AI then deconstructs the code, identifies its core functions, and generates a detailed report with Indicators of Compromise (IoCs) and TTPs (Tactics, Techniques, and Procedures) within minutes. This rapid analysis allows security teams to quickly develop and deploy countermeasures across their organizations.

Cybersecurity FAQ

What are AI Cybersecurity tools?

AI Cybersecurity tools are advanced security solutions that use machine learning (ML) and artificial intelligence to detect, prevent, and respond to cyber threats. Unlike traditional security systems that rely on predefined rules and signatures, AI tools analyze vast amounts of data to learn normal behavior patterns. This allows them to identify and flag anomalies that could indicate new, unknown, or sophisticated attacks (like zero-day threats) in real-time, making security more proactive and adaptive.

How do I choose the right AI Cybersecurity tool?

Choosing the right tool depends on your specific needs. Consider these key factors:

  • Integration: Ensure the tool can integrate smoothly with your existing security infrastructure, such as SIEM, SOAR, and firewalls.
  • Detection Accuracy: Evaluate its effectiveness in detecting threats and, importantly, its false positive rate. A high rate of false alarms can overwhelm your security team.
  • Scope of Automation: Determine what level of automated response you require. Some tools only provide alerts, while others can automatically take action like quarantining a device.
  • Data Sources: Check what data sources the tool can analyze (e.g., network traffic, endpoint logs, cloud logs, user activity) to ensure comprehensive coverage for your environment.
What's the difference between AI Cybersecurity and traditional antivirus?

The primary difference lies in their detection methods. Traditional antivirus software is reactive; it relies on a database of known malware signatures to identify threats. If a virus isn't in its database, it may not be detected. AI Cybersecurity, on the other hand, is proactive. It uses behavioral analysis to establish a baseline of normal activity and then looks for deviations. This allows it to detect novel, unknown (zero-day), and polymorphic malware that signature-based systems would miss, as it focuses on malicious *behavior* rather than a known *file*.

What are the main functions of AI in cybersecurity?

AI serves several critical functions in modern cybersecurity, transforming it from a reactive to a proactive discipline. Key functions include:

  • Real-time Threat Detection: Analyzing data streams to identify ongoing attacks, including zero-day exploits.
  • User and Entity Behavior Analytics (UEBA): Detecting insider threats or compromised accounts by spotting anomalous behavior.
  • Security Orchestration, Automation, and Response (SOAR): Automating routine security tasks and incident response workflows to reduce manual effort and response times.
  • Vulnerability Prioritization: Using predictive analytics to identify which vulnerabilities are most likely to be exploited, helping teams focus their efforts.
  • Advanced Phishing and Malware Analysis: Analyzing content and code with a level of sophistication that surpasses traditional methods.
Who benefits most from using AI Cybersecurity tools?

While any organization can benefit, those who gain the most are typically large enterprises or organizations in highly regulated, data-sensitive industries. This includes:

  • Financial Institutions: To protect against fraud, insider threats, and secure vast amounts of sensitive customer data.
  • Healthcare Organizations: To secure patient records (EHR) and comply with regulations like HIPAA.
  • E-commerce Platforms: To protect customer payment information and prevent account takeover attacks.
  • Government Agencies: To defend critical infrastructure and national security data from sophisticated state-sponsored attacks.

Essentially, any organization with a large attack surface, complex IT environment, and a small security team relative to its size will see significant value from the automation and advanced detection capabilities of AI.