ToolMage
Sign in

Best 3 Code Analysis AI tools for Development

Popular Code Analysis AI tools in Development include Gitmore, Ozgar, and SecVibe, helping you work more efficiently.

SecVibe

SecVibe

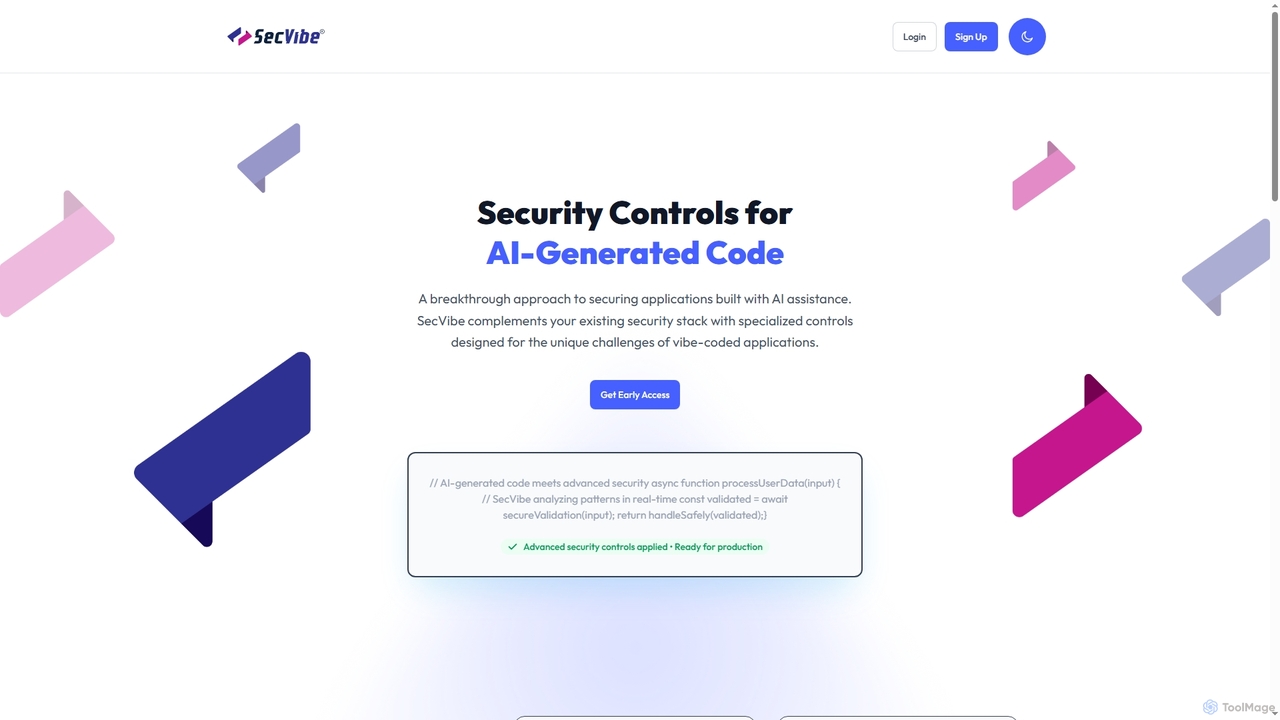
SecVibe is a cutting-edge security platform designed to protect applications built with AI-generated code. It offers specialized controls, real-time analysis, and context-aware mechanisms to identify and mitigate unique security vulnerabilities often missed by traditional tools. SecVibe seamlessly integrates with existing security stacks, enhancing overall application security for modern, AI-assisted development workflows without compromising speed.

Code Analysis
Visits 6.4KFavorites 57Likes 43
Gitmore
Freemium

Gitmore

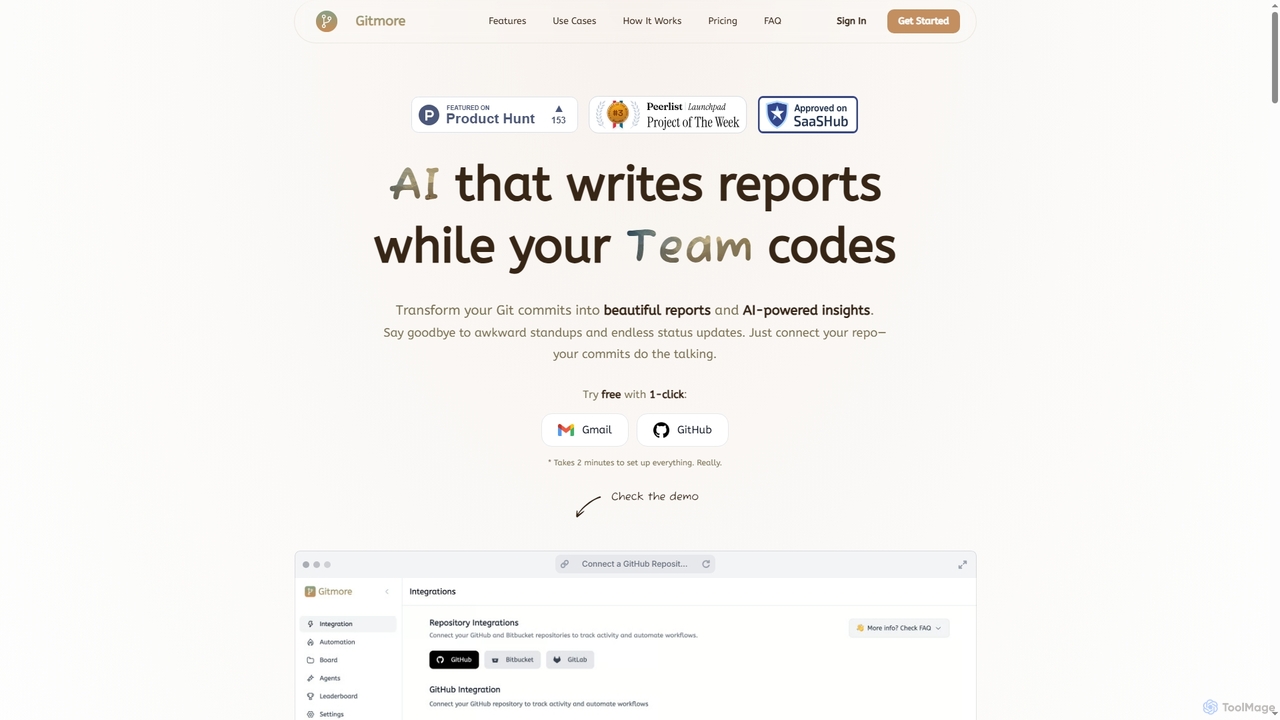
Gitmore is an AI-powered tool that automates technical team reporting and engineering updates. It transforms Git commits into intelligent reports and insights, eliminating manual status updates and standup meetings for development teams using GitHub, GitLab, or Bitbucket.

Productivity
Visits 14KFavorites 111Likes 111
Ozgar

Ozgar

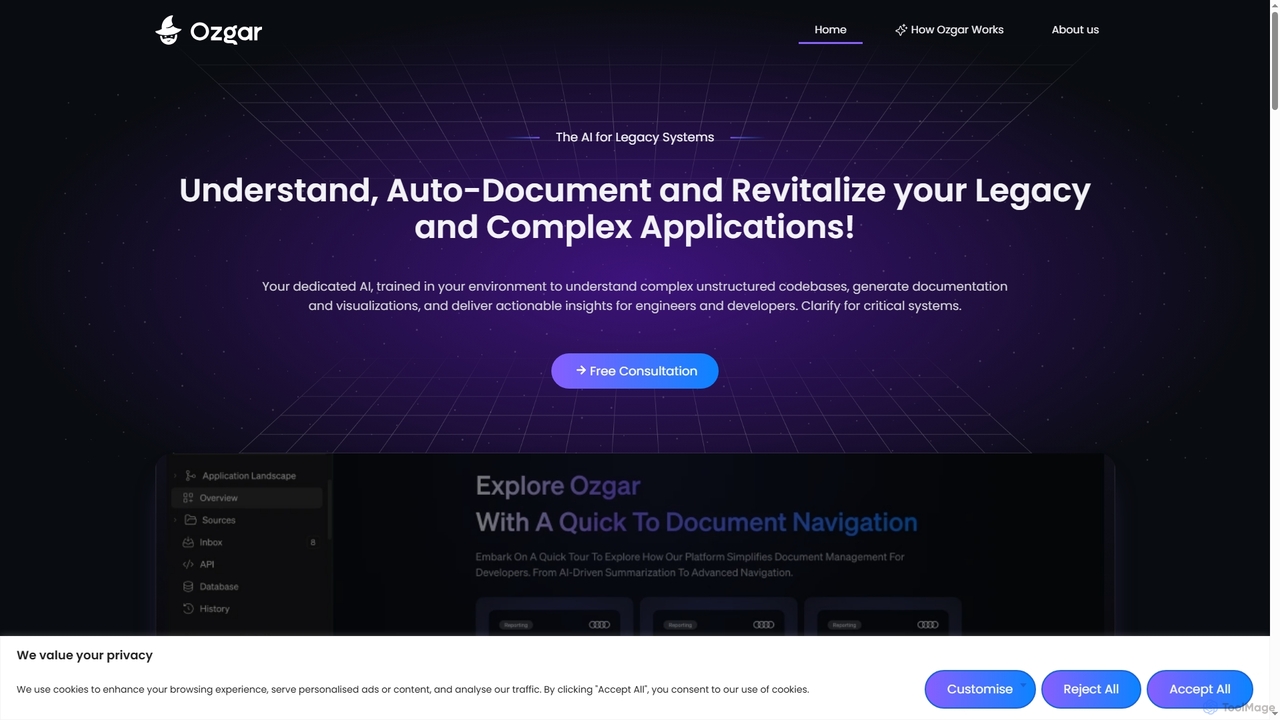
Ozgar is an enterprise code intelligence platform designed to understand, auto-document, and revitalize legacy and complex software systems. It leverages advanced AI to transform unstructured codebases into a smart, searchable knowledge hub, providing developers and teams with instant insights, automated documentation, and enhanced code navigation. Ozgar aims to reduce technical debt, accelerate onboarding, and streamline maintenance without disrupting existing operations.

Code Analysis
Visits 10.5KFavorites 116Likes 114

About Code Analysis

Code Analysis tools are AI-powered solutions designed to automatically inspect source code for potential issues, vulnerabilities, and quality improvements. These tools leverage advanced algorithms to understand code structure and logic, providing developers with actionable insights to enhance software reliability and maintainability. They play a crucial role in modern software development by integrating seamlessly into CI/CD pipelines, ensuring code quality from the earliest stages.

Core Features

  • Static Code Analysis: Automatically scans code without execution to identify bugs, security flaws, and style violations.
  • Dynamic Code Analysis: Monitors code behavior during runtime to detect performance bottlenecks, memory leaks, and concurrency issues.
  • Security Vulnerability Detection: Identifies common security weaknesses like SQL injection, cross-site scripting (XSS), and insecure configurations.
  • Code Quality Metrics: Calculates metrics such as cyclomatic complexity, maintainability index, and duplication rate to assess code health.
  • Automated Refactoring Suggestions: Provides recommendations for improving code structure, readability, and efficiency.

Use Cases

Code Analysis tools are essential for development teams to maintain high standards of software quality and security. They are used to enforce coding standards across projects, identify and fix bugs early in the development cycle, and ensure compliance with industry regulations. These tools help reduce technical debt and improve collaboration among developers.

How to Choose

When selecting a Code Analysis tool, consider its compatibility with your programming languages and development environment. Evaluate its ability to integrate with your existing CI/CD pipelines and version control systems. Look for comprehensive reporting features, customizable rule sets, and the accuracy of its findings to minimize false positives.

Code Analysis use cases

1

Automated Bug Detection in Development Workflows

Software developers integrate AI-powered code analysis tools into their IDEs or CI/CD pipelines to automatically scan new code commits. This helps identify syntax errors, logical flaws, and potential runtime exceptions immediately, preventing bugs from reaching later stages of development and significantly reducing debugging time.

2

Enhancing Security Posture of Web Applications

Security engineers and development teams use code analysis tools to proactively scan web application source code for common vulnerabilities like SQL injection, XSS, and insecure API endpoints. The tools provide detailed reports and remediation suggestions, allowing developers to fix security flaws before deployment and comply with security standards.

3

Maintaining Code Quality and Standards Across Large Teams

Project leads and architects deploy code analysis tools to enforce consistent coding standards and best practices across large, distributed development teams. The tools automatically check for style violations, code complexity, and duplication, ensuring maintainability and readability, which is crucial for long-term project health and onboarding new team members.

4

Optimizing Performance of High-Traffic Backend Services

Backend developers utilize dynamic code analysis to monitor the runtime behavior of critical services under load. These tools identify performance bottlenecks, inefficient algorithms, and memory leaks that might not be apparent during static analysis. This allows for targeted optimizations, ensuring services remain responsive and scalable.

5

Assessing and Reducing Technical Debt in Legacy Systems

Teams managing legacy software use code analysis to gain insights into the existing codebase's health. The tools can pinpoint areas of high complexity, low test coverage, and excessive duplication, providing a clear roadmap for refactoring efforts. This helps prioritize technical debt reduction, making the system easier to maintain and evolve.

6

Ensuring Compliance with Industry Regulations (e.g., GDPR, HIPAA)

Organizations in regulated industries (finance, healthcare) employ code analysis tools to verify that their software adheres to specific data privacy and security regulations. The tools can detect patterns that violate compliance rules, such as improper data handling or logging of sensitive information, providing an audit trail and reducing legal risks.

Code Analysis FAQ

What are AI Code Analysis tools?

AI Code Analysis tools are software applications that use artificial intelligence, including machine learning and natural language processing, to automatically examine source code. They go beyond traditional static analysis by understanding code context and intent, identifying complex bugs, security vulnerabilities, and areas for quality improvement more effectively than manual reviews or simpler rule-based systems.

How do AI Code Analysis tools differ from traditional static analysis?

Traditional static analysis primarily relies on predefined rules and patterns to detect issues. AI Code Analysis, while often incorporating static analysis, enhances this by using machine learning to learn from vast codebases, identify subtle anomalies, and predict potential issues based on historical data. This leads to fewer false positives, more accurate vulnerability detection, and smarter suggestions for code improvement.

What are the key benefits of using AI Code Analysis in development?

The primary benefits include early detection of bugs and security vulnerabilities, which significantly reduces development costs and time. These tools also enforce coding standards, improve code quality and maintainability, and help reduce technical debt. By automating code reviews, they free up developers to focus on more complex tasks and innovation.

Which programming languages are typically supported by AI Code Analysis tools?

Most AI Code Analysis tools offer broad language support, covering popular languages like Python, Java, JavaScript, C, C++, Go, Ruby, and PHP. Many also support frameworks and libraries associated with these languages. When choosing a tool, it's crucial to verify its compatibility with your specific technology stack.

How can AI Code Analysis improve software security?

AI Code Analysis tools enhance software security by automatically scanning for a wide range of vulnerabilities, including OWASP Top 10 risks (e.g., injection flaws, broken authentication, sensitive data exposure). They can identify insecure coding practices, misconfigurations, and potential attack vectors, providing developers with actionable insights to patch weaknesses before deployment, thereby strengthening the application's overall security posture.