
Binarly Overview
Binarly is a revolutionary binary risk intelligence platform designed to secure the entire software and firmware supply chain. In a landscape where traditional security tools fall short by merely mapping known vulnerabilities (CVEs), Binarly goes deeper. It analyzes the binary code itself—the final product that gets shipped and deployed—to understand its behavior and structure. This approach allows it to uncover not just known threats but entire classes of yet-undisclosed vulnerabilities, firmware implants, and malicious code with near-zero false positives. The platform is powered by a combination of modern static analysis, machine learning, and the deep expertise of its research team, which has a track record of discovering critical vulnerabilities like LogoFAIL.
The core mission of Binarly is to shift security left, embedding it directly into the development and procurement lifecycle. It addresses the critical gaps left by source-code-only analysis, as vulnerabilities can be introduced during compilation, linking, or through third-party dependencies. By providing comprehensive visibility into what's inside your binaries, Binarly empowers developers, security teams, and organizations to proactively manage risk, ensure compliance, and protect their infrastructure from the foundational level up.
How to use Binarly
Getting started with Binarly is a consultative process designed to tailor the solution to your specific needs. The typical workflow is as follows:
- Initial Consultation: Begin by booking a demo through the Binarly website. Their team of security experts will work with you to evaluate your current supply chain security posture and identify key risk areas.
- Integration: The Binarly Transparency Platform is designed for seamless integration into your existing workflows. It can be connected to your CI/CD (Continuous Integration/Continuous Deployment) pipeline to automate security scanning for every new build.
- Automated Analysis: Once integrated, Binarly automatically scans and analyzes binaries. This includes firmware (BIOS/UEFI), software executables, and container images. The platform does not require access to your source code.
- Risk Intelligence & Reporting: The platform generates detailed reports on its findings. This includes identified vulnerabilities (rated by CVSS), malicious code, transitive dependencies, license compliance issues, and insecure cryptographic patterns. Its AI-powered analysis provides context and impact assessment.
- Vulnerability Resolution: Binarly provides prescriptive and verified fixes for discovered vulnerabilities, making the resolution process faster and more efficient for development teams. This helps in quickly patching issues and preventing security regressions.
- Continuous Monitoring: With continuous assessment, you can maintain a high level of security, demonstrate compliance with legal and security frameworks, and stay ahead of emerging threats.
Core Features of Binarly
- Advanced Binary Risk Intelligence: Goes beyond CVE matching to detect entire classes of vulnerabilities, firmware implants, and malicious code by analyzing code execution behavior.
- Software Supply Chain Management: Automates the creation and validation of Software Bill of Materials (SBOMs), identifying all direct, static, and transitive dependencies to reveal the true composition of your software.
- AI-Assisted Vulnerability Management: Utilizes AI to analyze vulnerabilities, assess their real-world impact, and perform reachability analysis, which drastically reduces false positives and helps prioritize critical issues.
- Post-Build Security Automation: Integrates into CI/CD pipelines to detect common coding errors, insecure cryptographic patterns, and embedded secrets before deployment.
- Change and Dependency Analysis: Instantly compares different versions of a binary to understand changes, verify that security mitigations are applied, and catch regressions without needing source code.
- Continuous Compliance and Reporting: Continuously monitors for license compliance and helps generate reports to demonstrate due diligence for legal and security frameworks.
- Prescriptive Fixes: Offers actionable and verified recommendations to help developers resolve identified security defects quickly and effectively.
Use Cases for Binarly
Binarly is essential for any organization concerned with the integrity of its software and hardware. Key use cases include:
- Firmware Security: Device manufacturers and enterprises can scan BIOS/UEFI and BMC firmware to find and fix deep-level vulnerabilities before they can be exploited by attackers for persistent control.
- Software Supply Chain Security: Companies can vet third-party software and open-source components, ensuring they are free from backdoors, malware, or critical vulnerabilities before integration.
- DevSecOps Integration: Development teams can integrate Binarly into their CI/CD pipelines to automate security testing, catching and fixing vulnerabilities early in the development lifecycle.
- Vendor Risk Management: Procurement and security teams can use Binarly to hold vendors accountable by verifying the security claims of the software and devices they purchase.
- Incident Response and Forensics: Security analysts can use Binarly to analyze suspicious binaries to understand their functionality and identify hidden threats.
Advantages of Binarly
Binarly offers a distinct advantage over conventional security solutions:
- Detects the Unknown: Its primary strength is the ability to find zero-day vulnerabilities and novel threats that signature-based tools miss.
- Near-Zero False Positives: By understanding the context and reachability of a vulnerability, Binarly eliminates the alert fatigue common with other scanners, allowing teams to focus on real threats.
- Source Code Agnostic: Analysis is performed on the final binary, providing a true picture of the deployed software and overcoming the lack of access to proprietary source code.
- Actionable Intelligence: Instead of just flagging problems, Binarly provides clear, verified fixes, accelerating remediation cycles.
- Research-Driven Expertise: The platform is backed by a world-class research team responsible for discovering major industry-wide vulnerabilities, ensuring its detection capabilities are always at the cutting edge.
Pricing and Plans
Binarly operates on a customized pricing model tailored to the specific needs of each organization. There are no public pricing tiers listed on the website. To get a quote, interested parties are encouraged to "Book a demo" or "Talk to our team." The process involves a consultation to understand your requirements, such as the volume of analysis and integration needs, after which a custom package is proposed. Binarly also offers a "Free scan" option, allowing potential users to experience a sample of the platform's capabilities.
Traffic
Latest traffic
Status
Monthly traffic trend
- 2025-9: 28.0K
- 2026-1: 22.0K
- 2026-2: 18.2K
- 2026-3: 15.7K
- 2026-4: 32.9K
- 2026-5: 21.0K
Geography
Top 5 countries / regions
- 🇺🇸United States35.4%
- 🇻🇳Vietnam20.2%
- 🇮🇳India16.8%
- 🇷🇺Russia16.5%
- 🇧🇷Brazil11.1%
Top keywords
| Keyword | Cost per click |
|---|---|
| binarily | $0.00 |
| binarly | $0.00 |
| bypass tmr and secure boot bat | $0.00 |
| is secure boot a vendor locking tool | $0.00 |
| leaked secrets photo | $0.00 |
Binarly Alternatives

ethiack
Ethiack is an autonomous ethical hacking platform that combines AI-powered automated penetration testing with elite human hackers. It provides continuous 24/7 security testing to identify and prioritize vulnerabilities across your entire digital infrastructure, helping you stay compliant and secure before threats are exploited.
Testing
Aquilax
AquilaX is an AI-powered DevSecOps platform designed to secure software throughout the development lifecycle. It integrates seamlessly into CI/CD pipelines, offering a suite of 12 advanced scanners for vulnerabilities, secrets, and compliance. With its self-learning AI model, AquilaX dramatically reduces false positives, provides actionable remediation steps, and empowers teams to ship secure code with confidence and speed.
Code Security
win3zz
win3zz is an AI-powered cybersecurity platform designed for proactive threat detection and vulnerability management. It automates penetration testing, scans for vulnerabilities across web, mobile, and network assets, and provides AI-driven code analysis to help developers and security teams build and maintain secure applications.
Code Analysis
Cryptosense
An enterprise-grade platform, now part of SandboxAQ's Security Suite, that provides automated discovery, analysis, and management of your entire cryptographic infrastructure. It helps organizations achieve crypto-agility and migrate to post-quantum cryptography (PQC) securely.
Code Analysis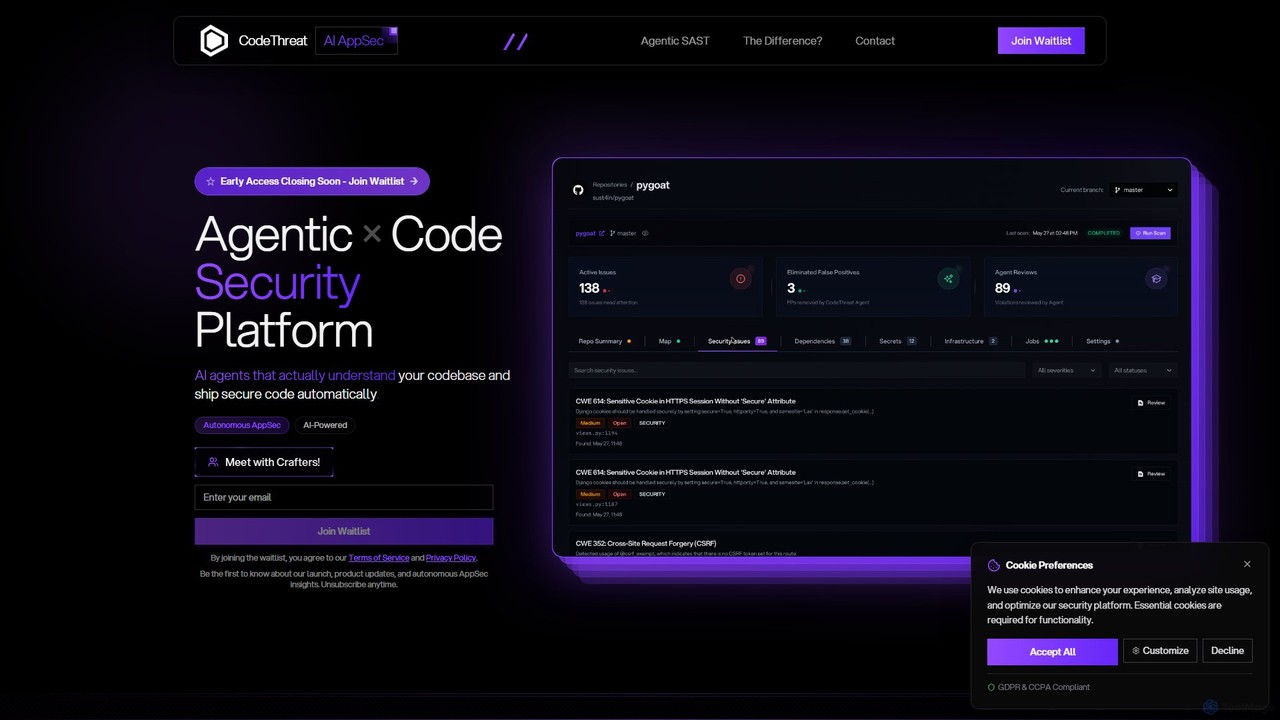
CodeThreat
CodeThreat is an AI-powered Agentic SAST platform that acts as an autonomous application security engineer. It deeply understands your codebase, identifies contextual vulnerabilities, eliminates false positives, and automatically remediates threats, ensuring you ship secure code without slowing down development.
Code SecurityBinarly Categories
Binarly Embed Widget
Copy this embed code to place the badge on your blog, article, or product site and send readers directly to this ToolMage detail page.

Related AI tools
EdgeBit
EdgeBit is an AI-powered platform for real-time software supply chain security. It automates Software Composition Analysis (SCA) and dependency management, identifying and fixing vulnerabilities by connecting build pipelines to runtime environments. It uses AI to propose low-risk, automated dependency upgrades, saving developer time and enhancing security.
Code SecurityAquilax
AquilaX is an AI-powered DevSecOps platform designed to secure software throughout the development lifecycle. It integrates seamlessly into CI/CD pipelines, offering a suite of 12 advanced scanners for vulnerabilities, secrets, and compliance. With its self-learning AI model, AquilaX dramatically reduces false positives, provides actionable remediation steps, and empowers teams to ship secure code with confidence and speed.
Code SecurityCryptosense
An enterprise-grade platform, now part of SandboxAQ's Security Suite, that provides automated discovery, analysis, and management of your entire cryptographic infrastructure. It helps organizations achieve crypto-agility and migrate to post-quantum cryptography (PQC) securely.
Code AnalysisCodeThreat
CodeThreat is an AI-powered Agentic SAST platform that acts as an autonomous application security engineer. It deeply understands your codebase, identifies contextual vulnerabilities, eliminates false positives, and automatically remediates threats, ensuring you ship secure code without slowing down development.
Code Security
Corgea
Corgea is an AI-powered application security (AppSec) platform that unifies SAST, SCA, secrets scanning, and more. It intelligently triages vulnerabilities, reducing false positives by up to 90%, and automatically generates code fixes. Designed for modern development teams, Corgea integrates seamlessly into developer workflows (GitHub, Azure DevOps), enabling them to secure every commit without sacrificing speed.
Code Security
Jyek
Jyek is an AI agent platform that understands objectives, creates execution plans, uses tools, and delivers verifiable results for complex, multi-step tasks.
Automation
Npmscan
Npmscan is an AI-powered security scanner designed to protect developers from malicious npm packages. It provides real-time threat detection, deep dependency analysis, and instant alerts to prevent supply chain attacks, crypto-draining malware, and other vulnerabilities.
Security
Patchifi
Patchifi is a cloud-native platform that automates endpoint management, patching, and compliance for IT teams and Managed Service Providers (MSPs). It streamlines software deployment, enhances security, and boosts IT efficiency by up to 49% through intelligent automation, eliminating manual scripts and complexity.
Regulatory Reporting
ZeroRisk
ZeroRisk offers a done-for-you vendor risk management service, automating daily monitoring, compliance mapping, and audit-ready reporting for third-party vendors. It helps businesses effortlessly meet global regulatory standards like GDPR, ISO 27001, SOC 2, NIS2, DORA, and CRA, eliminating manual spreadsheets and audit stress.
Vendor Management
cyberriskai
CyberRiskAI is an AI-powered platform designed for proactive cybersecurity risk management. It leverages predictive threat intelligence and automated analysis to help businesses identify, quantify, and mitigate cyber threats. The platform provides real-time risk scoring, vulnerability assessments, and actionable remediation guidance, enabling organizations to strengthen their security posture and ensure regulatory compliance.
Complianceethiack
Ethiack is an autonomous ethical hacking platform that combines AI-powered automated penetration testing with elite human hackers. It provides continuous 24/7 security testing to identify and prioritize vulnerabilities across your entire digital infrastructure, helping you stay compliant and secure before threats are exploited.
Testing
Snyk
Snyk is an AI-powered developer security platform that helps businesses build software securely. It proactively finds and fixes vulnerabilities in custom code, open-source dependencies, containers, and Infrastructure as Code (IaC) throughout the entire development lifecycle, from IDE to production.
Code Security
Lakera
Lakera is an AI-native security platform designed to protect Generative AI applications from threats like prompt injection, data leakage, and compliance violations. It offers real-time runtime protection, continuous threat intelligence powered by the world's largest AI red team, and easy integration with a single line of code. Trusted by enterprises like Dropbox, Lakera secures AI agents and applications across all major models and languages with ultra-low latency.
Api
Nightfall AI
Nightfall AI is an all-in-one, AI-powered Data Loss Prevention (DLP) platform. It automatically discovers, classifies, and protects sensitive data across SaaS applications, GenAI tools, email, and endpoints, preventing data leaks and managing insider risks with high accuracy.
Api
AiPrise
AiPrise is an AI-powered global verification platform that automates Know Your Customer (KYC) and Know Your Business (KYB) processes. It helps businesses mitigate risk, prevent fraud, and ensure compliance through a single, customizable API. The platform offers comprehensive identity verification, fraud scoring, and a compliance co-pilot to streamline onboarding and scale operations globally.
Fintech
Binarly Comments (0)
Sign in to comment.
Sign inNo comments yet.