
equixly Overview
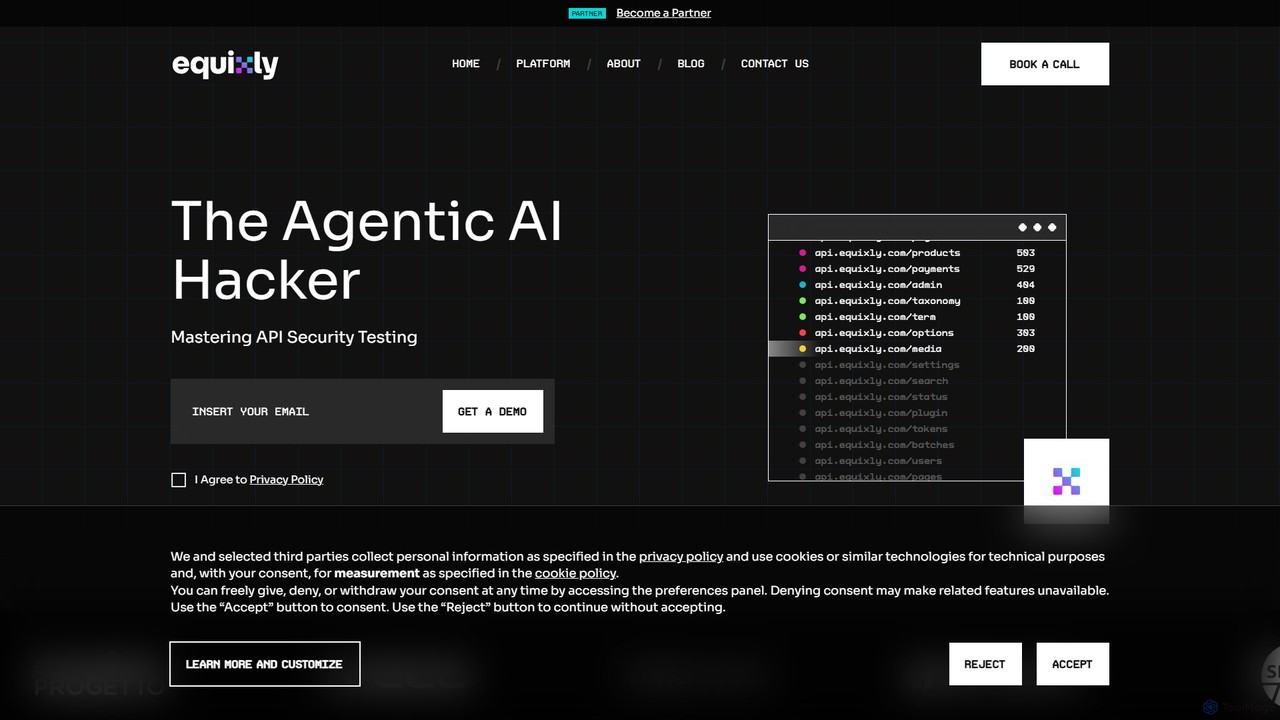
Equixly presents itself as 'The Agentic AI Hacker,' a sophisticated platform engineered to redefine and master API security. Born from the deep expertise of cybersecurity veterans, Equixly leverages a proprietary AI and Machine Learning engine to automate the complex and critical process of API penetration testing. It is designed to function like an ethical hacker, proactively identifying and assessing vulnerabilities before malicious actors can exploit them. The platform operates on a three-pronged approach: Map, Attack, and Compliance.
First, it meticulously maps your entire API attack surface, providing a complete inventory of your API landscape. This includes discovering shadow APIs and uncatalogued endpoints, classifying operations, and understanding the data traversing through them. This ensures 100% coverage, giving organizations a clear view of their potential risks.
Next, Equixly launches automated attacks on your APIs. These tests are not random; they are intelligent simulations based on the most critical security risks, including the OWASP Top 10 for APIs. The AI engine analyzes both requests and responses to uncover not just technical flaws but also complex business logic vulnerabilities that traditional scanners often miss. This breach simulation helps to understand the real-world impact of potential exploits.
Finally, the platform simplifies the compliance process. It generates clear, actionable reports that detail security risks, highlight sensitive data exposure, and provide guidance for rapid remediation. This transparent reporting helps organizations track their security posture over time and meet regulatory requirements with ease.
How to use equixly
Using Equixly is designed to be an integrated and streamlined process for development and security teams:
- Onboarding and Integration: Start by integrating Equixly into your environment. This typically involves providing your API specifications (e.g., OpenAPI, Swagger) or allowing the platform's AI bots to automatically discover your API endpoints. The onboarding process is designed to be quick and simple.
- Map Attack Surface: Once connected, Equixly's AI automatically begins to map your entire API landscape. It inventories all endpoints, dependencies, and data flows, presenting a comprehensive view of your attack surface.
- Configure and Automate Testing: Configure your security testing parameters. You can initiate on-demand penetration tests or, more powerfully, schedule them to run continuously. By integrating Equixly into your CI/CD pipeline, security testing becomes an automated part of every build and release.
- Analyze and Remediate: Review the detailed reports generated after each scan. The reports provide a prioritized list of vulnerabilities, explain the potential impact, and offer clear recommendations for remediation. This allows developers to fix security flaws quickly and efficiently.
- Monitor for Compliance: Use the ongoing reports to monitor your security posture and demonstrate compliance with industry standards and regulations. The platform helps you track improvements and maintain a robust defense.
Core Features of equixly
- Agentic AI Hacker Engine: A proprietary AI that mimics the behavior of an ethical hacker to perform intelligent and context-aware security testing.
- Automated API Penetration Testing: Fully automates the process of API pen-testing, saving time and resources compared to manual methods.
- Continuous Security Integration: Seamlessly integrates into DevOps workflows (CI/CD pipelines) to enable a 'shift-left' approach to security.
- Comprehensive Attack Surface Mapping: Discovers and inventories all APIs, including shadow and undocumented endpoints, for complete visibility.
- OWASP Top 10 & Business Logic Testing: Executes attack scenarios based on the OWASP Top 10 API risks and identifies complex business logic vulnerabilities.
- Sensitive Data Exposure Analysis: Identifies endpoints that handle sensitive data (e.g., PII, credit card numbers) and assesses their security.
- Simplified Compliance and Reporting: Generates clear, actionable reports to aid in rapid remediation and demonstrate regulatory compliance.
- Scalable Cloud-Based Platform: A flexible and scalable solution that can handle the security needs of both small applications and large enterprise ecosystems.
Use Cases for equixly
Equixly is ideal for a variety of stakeholders concerned with application security:
- DevSecOps Teams: To embed automated security testing directly into the software development lifecycle (SDLC), catching vulnerabilities early and accelerating secure code releases.
- Cybersecurity Professionals: To automate routine API penetration testing, freeing up security analysts to focus on more advanced threat hunting and strategic initiatives.
- Enterprises in Regulated Industries: For sectors like banking (BFSI), healthcare, and e-commerce that need to ensure continuous API security and maintain compliance with standards like PCI-DSS and GDPR.
- Companies with Microservices Architectures: To manage the complexity and vast attack surface created by numerous interconnected APIs, ensuring each service is secure.
Advantages of equixly
Equixly offers significant advantages over traditional security measures:
- Speed and Efficiency: Drastically reduces the time required for penetration testing from weeks to minutes, enabling rapid development cycles.
- Proactive Security Posture: Moves security from a reactive, periodic check to a proactive, continuous process integrated into development.
- Deep Expertise: The platform is built by a team with extensive, hands-on experience in offensive security, AI, and large-scale system architecture.
- Cost Reduction: Lowers the high costs associated with manual pen-testing, security consultant fees, and the financial impact of data breaches.
- Developer-Centric: Empowers developers with the tools and insights they need to write more secure code from the start, fostering a culture of security.
Pricing and Plans
Equixly's pricing information is not publicly available on their website. As an enterprise-focused solution, they operate on a quote-based model. To get pricing details, interested parties are encouraged to contact the sales team or request a personalized demo through their website. This allows them to tailor a plan that fits the specific scale and needs of your organization.
Traffic
Latest traffic
Status
Monthly traffic trend
- 2025-9: 8.3K
- 2026-1: 23.7K
- 2026-2: 16.6K
- 2026-3: 17.5K
- 2026-4: 18.9K
- 2026-5: 22.2K
Geography
Top 5 countries / regions
- 🇮🇳India25.2%
- 🇮🇩Indonesia20.8%
- 🇮🇹Italy19.4%
- 🇺🇸United States17.8%
- 🇳🇱Netherlands16.8%
Top keywords
| Keyword | Cost per click |
|---|---|
| ai for hacking | $0.31 |
| curl gemini public without api key | $0.00 |
| equixly | $0.00 |
| hack ai | $0.40 |
| hacker ai | $0.98 |
equixly Alternatives

Akto
Akto is an AI-powered, agentic API security platform for modern application security teams. It automates the entire API security lifecycle, from discovery and inventory to testing and runtime protection. Using autonomous AI agents, Akto continuously monitors, tests, and secures APIs, identifying vulnerabilities, sensitive data exposure, and business logic flaws 50x faster than manual methods.
Api Security
Beagle Security
Beagle Security is an AI-powered, automated penetration testing tool for web applications and APIs. It helps businesses proactively identify and remediate security vulnerabilities by integrating seamlessly into the DevSecOps lifecycle. The platform offers comprehensive scanning, detailed reporting, compliance management (HIPAA, PCI DSS), and actionable, LLM-based recommendations to strengthen your application security posture.
Testing
Snyk
Snyk is an AI-powered developer security platform that helps businesses build software securely. It proactively finds and fixes vulnerabilities in custom code, open-source dependencies, containers, and Infrastructure as Code (IaC) throughout the entire development lifecycle, from IDE to production.
Code Security
Zerothreat
ZeroThreat is an AI-powered continuous penetration testing and DAST platform designed to secure web applications and APIs. It automates the detection of over 40,000 vulnerabilities, including OWASP Top 10 and CVEs, providing fast, accurate, and actionable security insights for developers and security teams.
Testing
ethiack
Ethiack is an autonomous ethical hacking platform that combines AI-powered automated penetration testing with elite human hackers. It provides continuous 24/7 security testing to identify and prioritize vulnerabilities across your entire digital infrastructure, helping you stay compliant and secure before threats are exploited.
Testingequixly Categories
equixly Embed Widget
Copy this embed code to place the badge on your blog, article, or product site and send readers directly to this ToolMage detail page.

Related AI tools
Akto
Akto is an AI-powered, agentic API security platform for modern application security teams. It automates the entire API security lifecycle, from discovery and inventory to testing and runtime protection. Using autonomous AI agents, Akto continuously monitors, tests, and secures APIs, identifying vulnerabilities, sensitive data exposure, and business logic flaws 50x faster than manual methods.
Api SecurityBeagle Security
Beagle Security is an AI-powered, automated penetration testing tool for web applications and APIs. It helps businesses proactively identify and remediate security vulnerabilities by integrating seamlessly into the DevSecOps lifecycle. The platform offers comprehensive scanning, detailed reporting, compliance management (HIPAA, PCI DSS), and actionable, LLM-based recommendations to strengthen your application security posture.
TestingZerothreat
ZeroThreat is an AI-powered continuous penetration testing and DAST platform designed to secure web applications and APIs. It automates the detection of over 40,000 vulnerabilities, including OWASP Top 10 and CVEs, providing fast, accurate, and actionable security insights for developers and security teams.
Testingethiack
Ethiack is an autonomous ethical hacking platform that combines AI-powered automated penetration testing with elite human hackers. It provides continuous 24/7 security testing to identify and prioritize vulnerabilities across your entire digital infrastructure, helping you stay compliant and secure before threats are exploited.
Testing
Casco
Casco is an autonomous security testing platform for AI systems. It acts as a continuous, always-on AI red team, proactively identifying and helping to fix vulnerabilities in AI agents, applications, and infrastructure before malicious attackers can exploit them, replacing periodic penetration testing with year-round automated monitoring.
Model Security
win3zz
win3zz is an AI-powered cybersecurity platform designed for proactive threat detection and vulnerability management. It automates penetration testing, scans for vulnerabilities across web, mobile, and network assets, and provides AI-driven code analysis to help developers and security teams build and maintain secure applications.
Code Analysis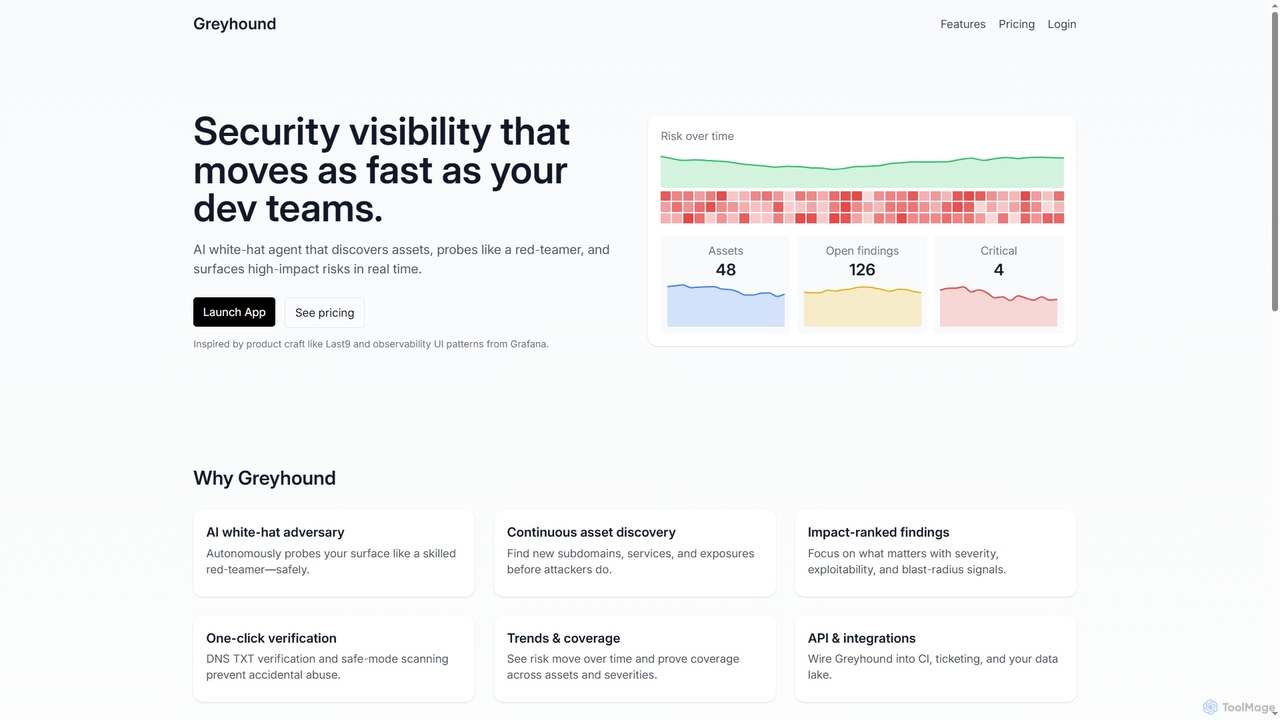
Greyhound
Greyhound is an AI-powered security platform that provides continuous scanning for web and cloud assets. It emulates a skilled attacker to autonomously discover assets, identify vulnerabilities, and provide impact-ranked findings with clear remediation steps, helping teams focus on critical risks.
Cloud Security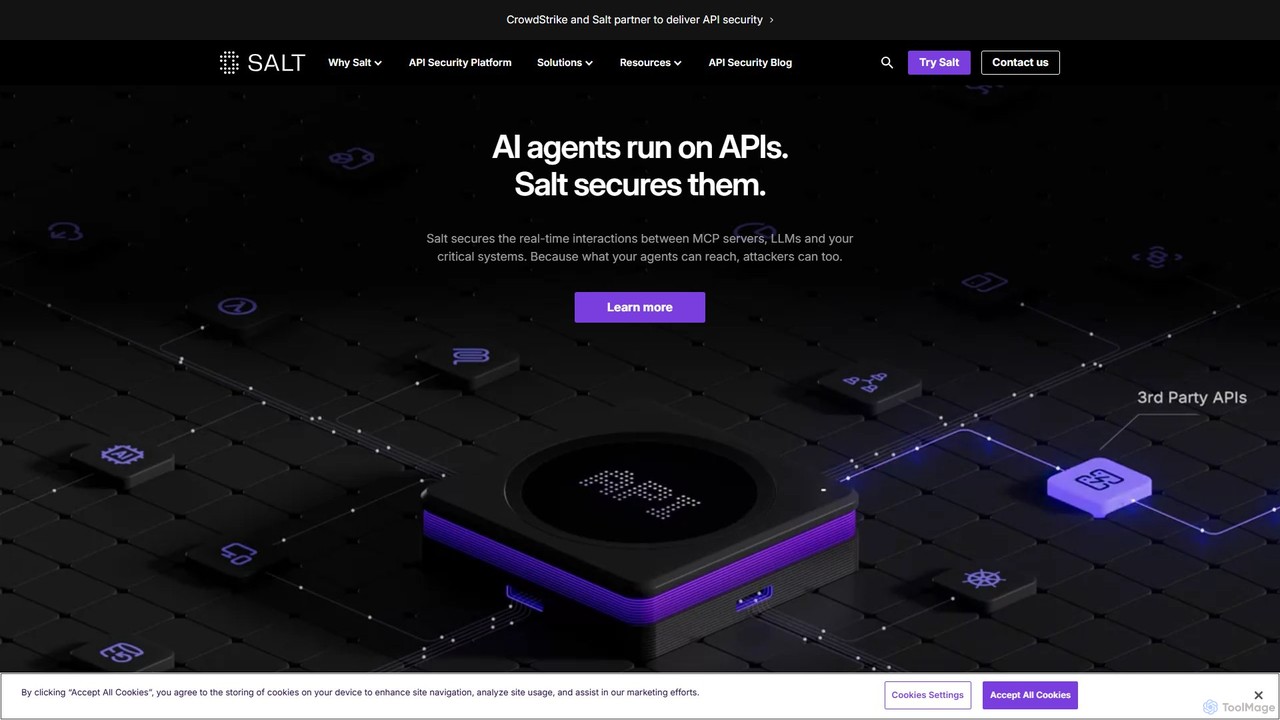
Salt Security
Salt Security is a pioneering AI-powered API security platform that provides comprehensive protection throughout the entire API lifecycle. It uses a patented, AI-driven engine to automatically discover all APIs, prevent sophisticated attacks in real-time, and ensure continuous compliance. The platform offers deep visibility, proactive threat detection, and automated governance to secure critical data and services against modern threats, including the OWASP API Top 10.
Testing
AppSanctuary
AppSanctuary is an AI-powered application security platform that automates vulnerability scanning, compliance checks, and threat detection. It helps developers and security teams build and maintain secure mobile and web applications by providing deep code analysis, actionable remediation advice, and seamless CI/CD integration.
Security & Compliance
OnSecurity
OnSecurity is an AI-augmented penetration testing platform that combines the efficiency of AI automation with the ingenuity of expert ethical hackers. It offers CREST-approved, continuous cybersecurity services, including pentesting, vulnerability scanning, and threat intelligence, all managed through a single, flexible subscription-based platform for faster, more accurate results.
Testing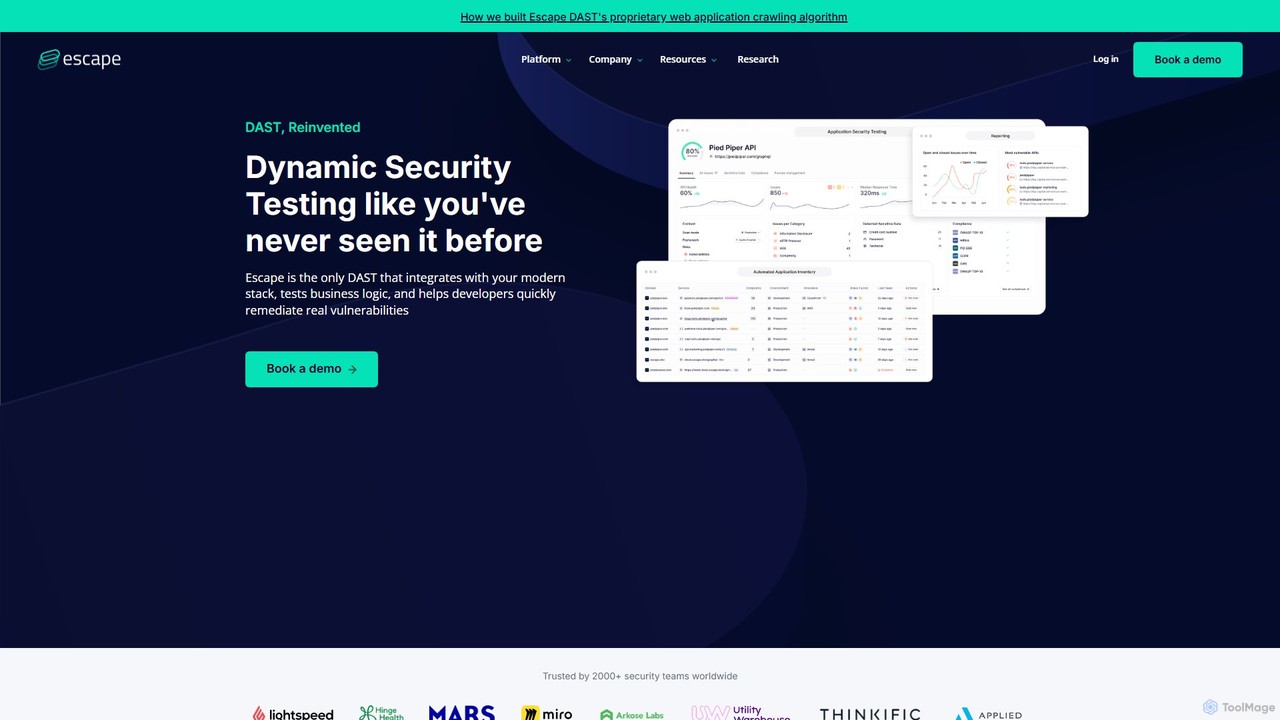
Escape
Escape is an AI-powered DAST (Dynamic Application Security Testing) tool specifically designed for modern applications. It focuses on securing APIs, especially GraphQL and REST, by testing for complex business logic vulnerabilities that traditional scanners often miss.
Security & Compliance
Metlo
Metlo is an open-source API security tool that you can set up in under 15 minutes. It automatically inventories your endpoints, detects malicious actors, and blocks threats like SQLi and XSS in real time with minimal performance impact.
Api Security
Quantum Network Monitor
An AI-powered network security and monitoring platform that automates vulnerability scanning, provides quantum readiness checks, and offers an interactive AI assistant. It simplifies enterprise-grade security with features like Nmap automation, anomaly detection, and comprehensive performance dashboards.
Testing
Veriom
Veriom is an autonomous AI security platform that acts as a neural layer for your infrastructure, SaaS, and AI systems. It goes beyond detection by mapping, prioritizing, and automatically fixing cybersecurity and compliance risks in real-time. By eliminating alert fatigue and manual triage, Veriom provides continuous assurance and proactive risk management.
Devsecops
Jyek
Jyek is an AI agent platform that understands objectives, creates execution plans, uses tools, and delivers verifiable results for complex, multi-step tasks.
Automation
equixly Comments (0)
Sign in to comment.
Sign inNo comments yet.