
Escape Overview
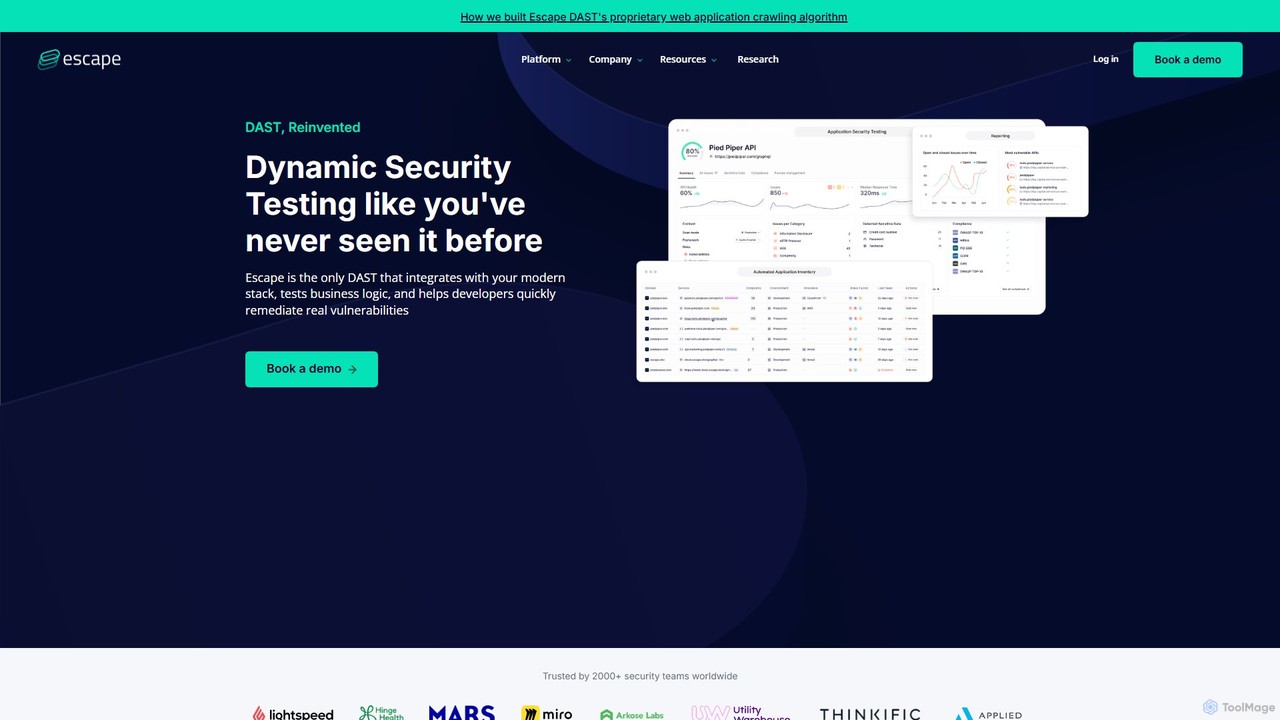
Escape is a next-generation application security platform that provides comprehensive Dynamic Application Security Testing (DAST) for modern technology stacks. Unlike traditional DAST tools built for monolithic web applications, Escape is purpose-built to secure the complex and interconnected world of APIs, with a special focus on GraphQL and REST APIs. It leverages advanced AI and a proprietary business logic security testing algorithm to uncover critical vulnerabilities that go beyond simple checks for missing headers or common configuration errors.
Praised by security teams across various industries like FinTech, Healthcare, and E-commerce, Escape helps organizations shift their security practices left. By integrating seamlessly into the development lifecycle (CI/CD), it empowers developers to identify and remediate security flaws in staging environments before they ever reach production. This proactive approach not only strengthens the security posture but also saves valuable time and resources by catching issues early.
How to use Escape
Using Escape is designed to be a seamless part of the development workflow:
- Integration: Connect Escape to your development environment. It offers seamless integration with popular CI/CD pipelines and tools like GitHub, GitLab, and Jenkins.
- API Discovery: Point Escape to your application. It automatically discovers your API endpoints, including GraphQL and REST, mapping out the entire attack surface.
- Configure & Scan: Configure the scan parameters. Escape's intelligent scanner then simulates hacker-like attacks, testing for a wide range of vulnerabilities, including broken access control, injection flaws, and complex business logic issues.
- Analyze Results: Review the detailed security report in the Escape dashboard. Each vulnerability is clearly explained, prioritized by severity, and includes the exact request and response to replicate the issue.
- Remediate: Utilize the actionable remediation guidance provided for each issue. The clear instructions help developers fix vulnerabilities quickly and effectively without needing to be security experts.
- Continuous Monitoring: Schedule automated, continuous scans to ensure your APIs remain secure as your application evolves.
Core Features of Escape
- Business Logic Security Testing: Utilizes a proprietary algorithm to find complex flaws in business logic, such as price manipulation in e-commerce or unauthorized data access.
- Comprehensive GraphQL Security: Offers specialized testing for GraphQL APIs, addressing common and advanced vulnerabilities like batching attacks, deep recursion, and access control bypasses. It also provides the open-source GraphQL Armor library for an added layer of defense.
- Automated API Discovery: Continuously scans and maps your entire API attack surface, ensuring no endpoint is left unprotected.
- CI/CD Integration: Integrates directly into your development pipeline, enabling a true DevSecOps approach by automating security testing on every code commit.
- Actionable Remediation: Provides clear, developer-friendly remediation advice for every vulnerability found, significantly reducing the time to fix.
- Near-Zero False Positives: The AI-powered engine is fine-tuned to provide accurate results, allowing security and development teams to focus on real threats.
- Support for Modern Stacks: Purpose-built for modern architectures, including microservices, SPAs, and various API protocols.
Use Cases for Escape
Escape is trusted by companies across multiple sectors:
- FinTech & Finance: Securing sensitive financial data and transaction APIs against fraud and data breaches.
- Healthcare: Ensuring patient data confidentiality and API integrity in compliance with regulations like HIPAA.
- E-commerce: Preventing business logic flaws that could lead to revenue loss, such as unauthorized discounts or inventory manipulation.
- Technology & SaaS: Protecting the core APIs of software products, ensuring tenant data isolation and platform stability.
- AdTech: Securing high-throughput APIs that handle large volumes of data and complex user interactions.
Advantages of Escape
Escape offers a significant advantage over traditional security tools:
- Deeper Testing: Goes beyond surface-level checks to test the application's business logic, where the most critical and unique vulnerabilities often reside.
- Developer-First: Designed to be used by developers, with clear reports and seamless integration that doesn't slow down development velocity.
- Fast Time-to-Value: Can be set up in minutes, providing a comprehensive scan of the API attack surface within the first hour.
- Specialized Expertise: A market leader in GraphQL security, addressing a critical gap left by many other security tools.
- Proactive Security: Enables teams to find and fix vulnerabilities in pre-production, drastically reducing the risk of a security breach.
Pricing and Plans
Escape offers enterprise-level plans tailored to the specific needs of each organization. Pricing is based on factors such as the number of applications, API complexity, and required features. To get a personalized quote and see the platform in action, potential customers are encouraged to book a live demo through the official website.
Traffic
Latest traffic
Status
Monthly traffic trend
- 2025-9: 46.1K
- 2026-1: 56.2K
- 2026-2: 34.7K
- 2026-3: 39.9K
- 2026-4: 35.5K
- 2026-5: 34.5K
Geography
Top 5 countries / regions
- 🇺🇸United States46.2%
- 🇮🇳India17.0%
- 🇫🇷France16.3%
- 🇻🇳Vietnam10.6%
- 🇩🇪Germany9.9%
Traffic sources
| Source type | Percentage |
|---|---|
Direct | 94.5% |
Referral | 5.5% |
Top keywords
| Keyword | Cost per click |
|---|---|
| access control models (rbac / abac) | $0.00 |
| agentic agent prompt for pentesting | $0.00 |
| best ai for pen testing | $0.00 |
| escape security | $0.00 |
| tools ตัวไหน scan owasp top 10 ได้ครบทุก domail | $0.00 |
Escape Alternatives

AppSanctuary
AppSanctuary is an AI-powered application security platform that automates vulnerability scanning, compliance checks, and threat detection. It helps developers and security teams build and maintain secure mobile and web applications by providing deep code analysis, actionable remediation advice, and seamless CI/CD integration.
Security & Compliance
deepchecks
Deepchecks is an end-to-end platform for evaluating, validating, and monitoring LLM-based applications. It helps AI teams define, measure, and validate AI progress, ensuring the release of high-quality, reliable applications by streamlining testing from development through CI/CD to production.
Analytics
Huntr
Huntr is the world's first bug bounty platform dedicated to securing the AI/ML ecosystem. It connects security researchers with open-source AI projects, enabling them to discover and report vulnerabilities in AI applications, libraries, and model file formats. Researchers earn financial rewards for validated findings, helping to ensure the safety and stability of critical AI technologies like PyTorch, TensorFlow, and Hugging Face Transformers.
Mlops
Zerothreat
ZeroThreat is an AI-powered continuous penetration testing and DAST platform designed to secure web applications and APIs. It automates the detection of over 40,000 vulnerabilities, including OWASP Top 10 and CVEs, providing fast, accurate, and actionable security insights for developers and security teams.
Testing
Netify
Netify is a network intelligence platform that provides deep visibility into network traffic through Deep Packet Inspection (DPI), cloud-based analytics, and data feeds. It helps businesses and IT professionals monitor, secure, and optimize their networks by identifying applications, detecting threats, and analyzing performance.
AnalyticsEscape Categories
Escape Embed Widget
Copy this embed code to place the badge on your blog, article, or product site and send readers directly to this ToolMage detail page.

Related AI tools
Zerothreat
ZeroThreat is an AI-powered continuous penetration testing and DAST platform designed to secure web applications and APIs. It automates the detection of over 40,000 vulnerabilities, including OWASP Top 10 and CVEs, providing fast, accurate, and actionable security insights for developers and security teams.
Testing
Akto
Akto is an AI-powered, agentic API security platform for modern application security teams. It automates the entire API security lifecycle, from discovery and inventory to testing and runtime protection. Using autonomous AI agents, Akto continuously monitors, tests, and secures APIs, identifying vulnerabilities, sensitive data exposure, and business logic flaws 50x faster than manual methods.
Api Security
ethiack
Ethiack is an autonomous ethical hacking platform that combines AI-powered automated penetration testing with elite human hackers. It provides continuous 24/7 security testing to identify and prioritize vulnerabilities across your entire digital infrastructure, helping you stay compliant and secure before threats are exploited.
Testing
Snyk
Snyk is an AI-powered developer security platform that helps businesses build software securely. It proactively finds and fixes vulnerabilities in custom code, open-source dependencies, containers, and Infrastructure as Code (IaC) throughout the entire development lifecycle, from IDE to production.
Code Security
Beagle Security
Beagle Security is an AI-powered, automated penetration testing tool for web applications and APIs. It helps businesses proactively identify and remediate security vulnerabilities by integrating seamlessly into the DevSecOps lifecycle. The platform offers comprehensive scanning, detailed reporting, compliance management (HIPAA, PCI DSS), and actionable, LLM-based recommendations to strengthen your application security posture.
Testing
Salt Security
Salt Security is a pioneering AI-powered API security platform that provides comprehensive protection throughout the entire API lifecycle. It uses a patented, AI-driven engine to automatically discover all APIs, prevent sophisticated attacks in real-time, and ensure continuous compliance. The platform offers deep visibility, proactive threat detection, and automated governance to secure critical data and services against modern threats, including the OWASP API Top 10.
Testing
equixly
Equixly is an agentic AI hacker platform designed for mastering API security. It automates penetration testing by mapping your entire API attack surface, launching attacks based on OWASP Top 10 risks, and simplifying compliance reporting. It helps developers and security teams to continuously test, identify, and remediate vulnerabilities within the CI/CD pipeline.
Security & Testing
Casco
Casco is an autonomous security testing platform for AI systems. It acts as a continuous, always-on AI red team, proactively identifying and helping to fix vulnerabilities in AI agents, applications, and infrastructure before malicious attackers can exploit them, replacing periodic penetration testing with year-round automated monitoring.
Model Security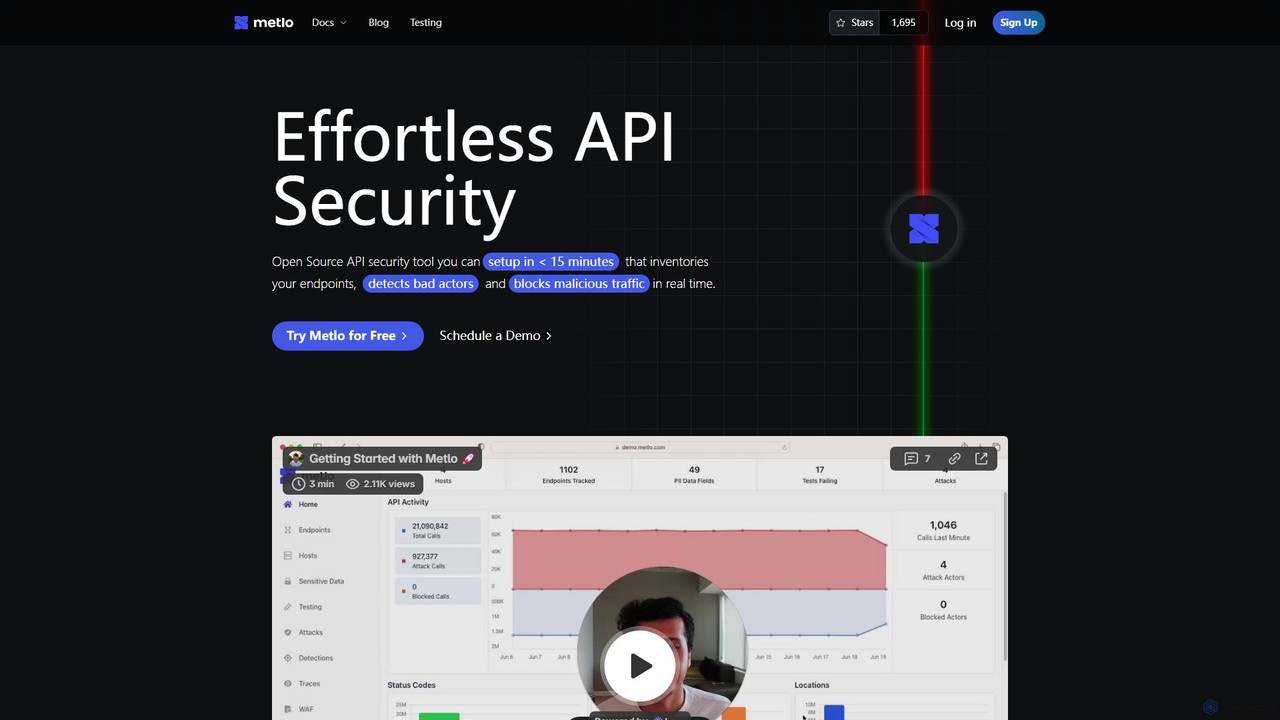
Metlo
Metlo is an open-source API security tool that you can set up in under 15 minutes. It automatically inventories your endpoints, detects malicious actors, and blocks threats like SQLi and XSS in real time with minimal performance impact.
Api Security
Npmscan
Npmscan is an AI-powered security scanner designed to protect developers from malicious npm packages. It provides real-time threat detection, deep dependency analysis, and instant alerts to prevent supply chain attacks, crypto-draining malware, and other vulnerabilities.
Security
DepsHub
DepsHub is an AI-powered platform that automates dependency management for development teams. It simplifies updates, performs security vulnerability scanning, and ensures license compliance, allowing developers to focus on coding while maintaining a secure and up-to-date codebase.
Code Management
win3zz
win3zz is an AI-powered cybersecurity platform designed for proactive threat detection and vulnerability management. It automates penetration testing, scans for vulnerabilities across web, mobile, and network assets, and provides AI-driven code analysis to help developers and security teams build and maintain secure applications.
Code AnalysisAppSanctuary
AppSanctuary is an AI-powered application security platform that automates vulnerability scanning, compliance checks, and threat detection. It helps developers and security teams build and maintain secure mobile and web applications by providing deep code analysis, actionable remediation advice, and seamless CI/CD integration.
Security & Compliance
Jyek
Jyek is an AI agent platform that understands objectives, creates execution plans, uses tools, and delivers verifiable results for complex, multi-step tasks.
Automationdeepchecks
Deepchecks is an end-to-end platform for evaluating, validating, and monitoring LLM-based applications. It helps AI teams define, measure, and validate AI progress, ensuring the release of high-quality, reliable applications by streamlining testing from development through CI/CD to production.
Analytics
Escape Comments (0)
Sign in to comment.
Sign inNo comments yet.