
DevOps Security Overview
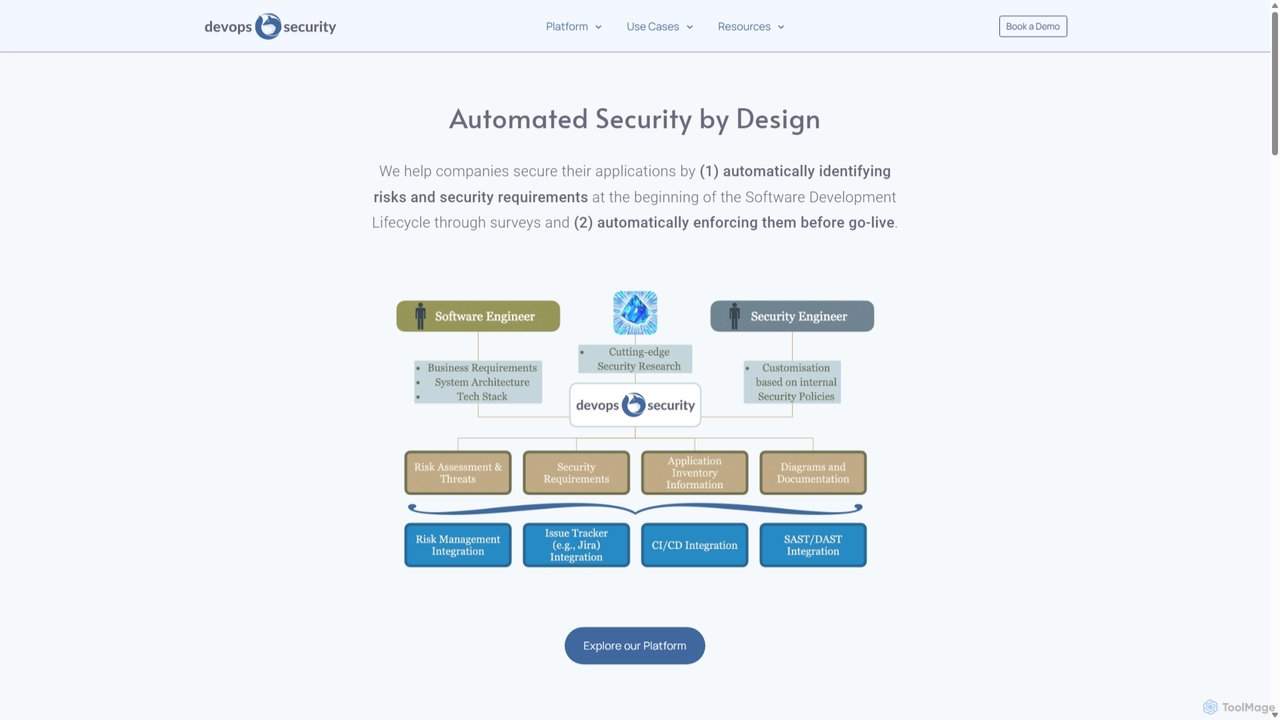
DevOps Security is a forward-thinking platform designed to embed security into the very fabric of the software development process. It addresses the common challenges faced by modern development and security teams, such as the lack of automation in risk assessment, the communication gap between developers and security experts, and the bottleneck of last-minute security reviews. By adopting a 'Security by Design' philosophy, the platform automates the identification of risks and security requirements at the earliest stages of the SDLC.
The core of the platform is its AI-native approach. It utilizes artificial intelligence to generate comprehensive security questionnaires, define precise security requirements, and even map out potential attack vectors relevant to a specific project. This AI-driven intelligence ensures that security measures are not only robust but also tailored and up-to-date with the evolving threat landscape. This proactive stance helps prevent vulnerabilities before they are ever written into code, saving significant time and resources down the line.
How to use DevOps Security
Using DevOps Security involves integrating its automated workflows into your existing development pipeline. The process is designed to be seamless and developer-centric:
- Integration: Connect the DevOps Security platform with your current SDLC toolchain, such as Jira, GitHub, Jenkins, or other CI/CD tools, using its robust API.
- Assessment Configuration: Define risk and security assessments. You can use the platform's expert-designed templates, leverage AI to generate project-specific questionnaires, or fully customize them to meet your organization's compliance and security standards.
- Automated Assessment: At the beginning of a new project or feature development, developers or project managers complete a brief, automated survey. The platform analyzes the responses to identify potential risks and determine the necessary security posture.
- Requirement Generation: Based on the assessment, the platform automatically generates a clear, actionable list of security requirements and tasks, assigning them directly to the development team.
- Continuous Enforcement: As development progresses, the platform automatically monitors the codebase and pipeline to enforce these requirements. It can be configured to block deployments that fail to meet critical security criteria, ensuring no insecure code reaches production.
- Centralized Monitoring: Security teams can use the centralized dashboard to gain full visibility into the security posture of all projects, track compliance, and manage policies across the organization.
Core Features of DevOps Security
- AI-Native Security Intelligence: Utilizes AI to generate dynamic questionnaires, context-aware security requirements, and potential attack vectors, providing a comprehensive security analysis.
- Automated Risk Assessment: Streamlines the process of identifying project risks early in the SDLC through automated, customizable surveys.
- SDLC Integration & Automation: Offers deep integrations with popular developer tools and CI/CD pipelines to automatically enforce security policies and requirements.
- Policy as Code: Allows security teams to define and manage security policies as code, enabling version control, collaboration, and scalability.
- Centralized Platform: Provides a single source of truth for defining, distributing, and monitoring risk and security assessments across all projects.
- Customization and API Access: Offers high flexibility to customize questionnaires and requirements, with full API access to integrate and automate all functionalities.
- Security Champion Empowerment: Designed to delegate security responsibilities to project teams, providing them with the tools and clarity needed to implement security effectively.
Use Cases for DevOps Security
DevOps Security is versatile and can be applied in various scenarios:
- Cloud-Native Application Development: Secure microservices and containerized applications from the ground up by embedding security checks throughout the CI/CD pipeline.
- Enterprise-Scale DevSecOps: Standardize and automate security practices across hundreds of development teams, ensuring consistent policy enforcement and reducing the burden on a central security team.
- Regulatory Compliance: Automate the implementation and verification of controls required by standards like GDPR, HIPAA, PCI-DSS, and SOC 2.
- Startups and SMEs: Establish a mature security program without a large, dedicated security team by leveraging automation and AI-driven expertise.
Advantages of DevOps Security
The platform offers significant advantages over traditional security approaches:
- Shift-Left Security: By identifying and addressing risks at the design phase, it dramatically reduces the cost and complexity of fixing vulnerabilities later.
- Increased Development Velocity: Automating security removes manual bottlenecks, allowing developers to build and ship secure software faster.
- Improved Collaboration: Bridges the gap between development and security teams by providing a common platform and clear, actionable guidance.
- Scalable Security: Enables organizations to scale their security efforts in line with their development growth without proportionally increasing security headcount.
- Proactive Threat Prevention: The AI-driven approach helps anticipate and mitigate potential threats before they become active risks.
Pricing and Plans
DevOps Security typically offers enterprise-level pricing tailored to the specific needs of an organization. Pricing models are often based on factors such as the number of developers, the number of projects, or the specific features required. As is common with B2B SaaS platforms in this space, specific pricing is not publicly listed. Interested parties are encouraged to contact the sales team for a personalized quote or to schedule a demo to explore the platform's capabilities.
DevOps Security Alternatives

Zerothreat
ZeroThreat is an AI-powered continuous penetration testing and DAST platform designed to secure web applications and APIs. It automates the detection of over 40,000 vulnerabilities, including OWASP Top 10 and CVEs, providing fast, accurate, and actionable security insights for developers and security teams.
Testing
SecVibe
SecVibe is a cutting-edge security platform designed to protect applications built with AI-generated code. It offers specialized controls, real-time analysis, and context-aware mechanisms to identify and mitigate unique security vulnerabilities often missed by traditional tools. SecVibe seamlessly integrates with existing security stacks, enhancing overall application security for modern, AI-assisted development workflows without compromising speed.
Code Analysis
Hoop.dev
Hoop.dev is an AI-powered access gateway providing developers with invisible security and admins with command-line control. It offers secure, auditable access to databases and servers, featuring real-time AI data masking, session recording, and streamlined approval workflows to enhance security without disrupting productivity.
Security
Aptori
Aptori is an AI-powered application security platform that acts as an autonomous AI Security Engineer. It proactively detects, triages, and fixes vulnerabilities across your code, APIs, applications, and cloud infrastructure. By embedding security into the software development lifecycle, Aptori helps teams accelerate releases, ensure compliance, and maintain a resilient security posture.
Code Review
Enforster AI
Enforster AI is an AI-native Static Application Security Testing (SAST) tool that analyzes code like a senior developer. It understands business logic and context to identify real vulnerabilities with 90% accuracy, reducing false positives by 60% and providing AI-generated fixes.
Code AnalysisDevOps Security Categories
DevOps Security Jobs
DevOps Security Embed Widget
Copy this embed code to place the badge on your blog, article, or product site and send readers directly to this ToolMage detail page.

Related AI tools
Zerothreat
ZeroThreat is an AI-powered continuous penetration testing and DAST platform designed to secure web applications and APIs. It automates the detection of over 40,000 vulnerabilities, including OWASP Top 10 and CVEs, providing fast, accurate, and actionable security insights for developers and security teams.
Testing
Jyek
Jyek is an AI agent platform that understands objectives, creates execution plans, uses tools, and delivers verifiable results for complex, multi-step tasks.
Automation
Aquilax
AquilaX is an AI-powered DevSecOps platform designed to secure software throughout the development lifecycle. It integrates seamlessly into CI/CD pipelines, offering a suite of 12 advanced scanners for vulnerabilities, secrets, and compliance. With its self-learning AI model, AquilaX dramatically reduces false positives, provides actionable remediation steps, and empowers teams to ship secure code with confidence and speed.
Code SecuritySecVibe
SecVibe is a cutting-edge security platform designed to protect applications built with AI-generated code. It offers specialized controls, real-time analysis, and context-aware mechanisms to identify and mitigate unique security vulnerabilities often missed by traditional tools. SecVibe seamlessly integrates with existing security stacks, enhancing overall application security for modern, AI-assisted development workflows without compromising speed.
Code Analysis
Pwnus
Pwnus is an AI-powered enterprise cybersecurity platform offering next-generation solutions for automated penetration testing, intelligent threat modeling, and comprehensive risk management. It seamlessly integrates with existing infrastructure to provide continuous security monitoring, compliance management, and third-party risk assessment, safeguarding organizations from evolving cyber threats with advanced AI algorithms and machine learning.
Penetration TestingEnforster AI
Enforster AI is an AI-native Static Application Security Testing (SAST) tool that analyzes code like a senior developer. It understands business logic and context to identify real vulnerabilities with 90% accuracy, reducing false positives by 60% and providing AI-generated fixes.
Code Analysis
GenieEngage
GenieEngage is a DevOps-as-a-Service partner providing expert solutions in DevOps, DevSecOps, and GitOps. It helps businesses accelerate software delivery, enhance security, and scale infrastructure on clouds like AWS, Azure, and GCP, offering a full team of experts as a cost-effective alternative to in-house hiring.
Infrastructure Management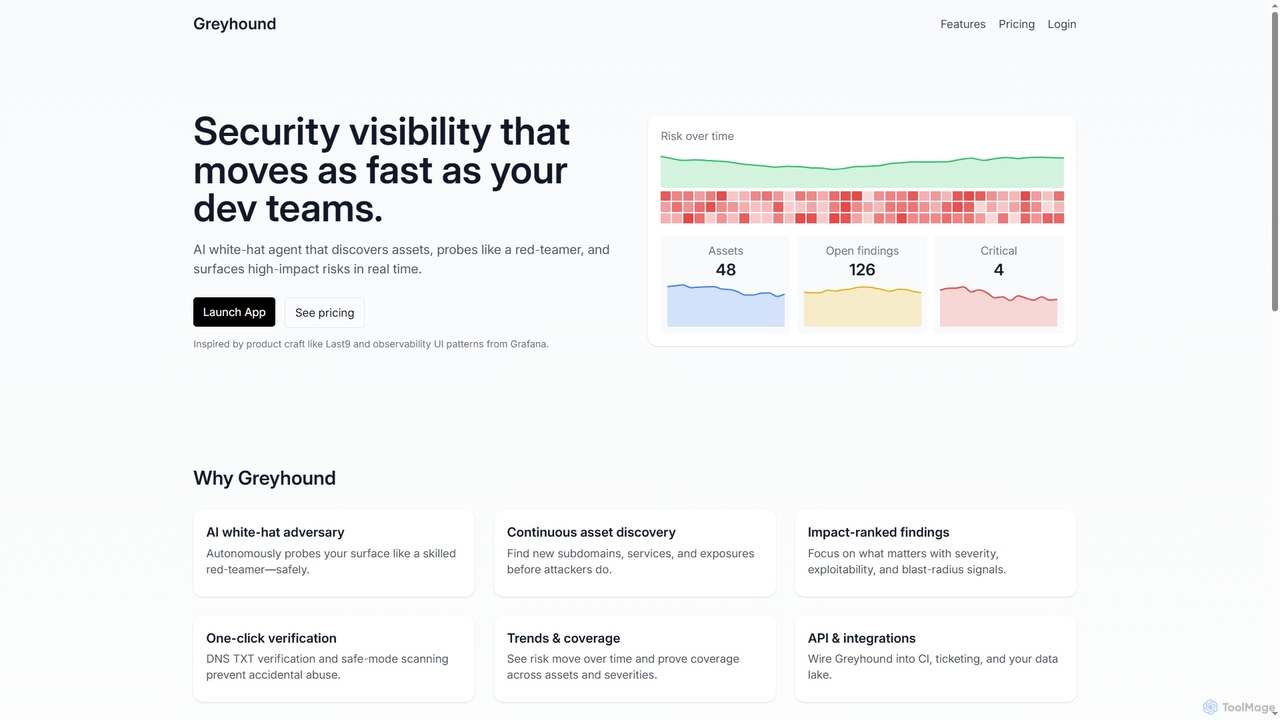
Greyhound
Greyhound is an AI-powered security platform that provides continuous scanning for web and cloud assets. It emulates a skilled attacker to autonomously discover assets, identify vulnerabilities, and provide impact-ranked findings with clear remediation steps, helping teams focus on critical risks.
Cloud SecurityHoop.dev
Hoop.dev is an AI-powered access gateway providing developers with invisible security and admins with command-line control. It offers secure, auditable access to databases and servers, featuring real-time AI data masking, session recording, and streamlined approval workflows to enhance security without disrupting productivity.
Security
CipherClaw
CipherClaw is an autonomous AI security agent that proactively scans your codebase for vulnerabilities, performs root cause analysis across dependencies using advanced causal graph and abstract geometric analysis, and autonomously generates and deploys production-ready patches. Designed for modern, AI-generated development workflows, it integrates seamlessly with ecosystems like OpenClaw, NVIDIA Nemo Claw, Lovable, and n8n.
Code Generation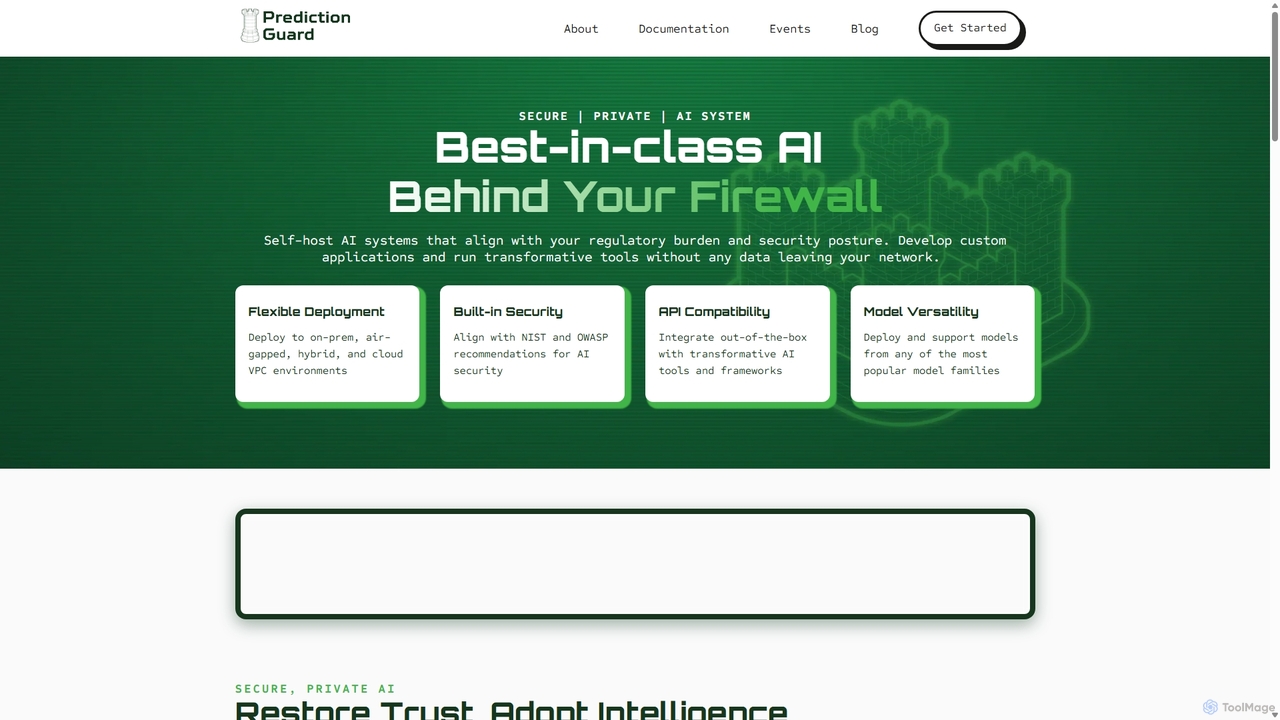
Prediction Guard
Prediction Guard is an enterprise-grade AI platform that allows organizations to deploy, manage, and scale large language models (LLMs) securely behind their own firewall. It offers flexible deployment options, including on-premise, air-gapped, and private cloud, ensuring complete data privacy and control. With an OpenAI-compatible API, it enables seamless integration with existing tools and frameworks like LangChain and LlamaIndex, making it ideal for regulated industries such as healthcare, defense, and finance.
Platform As A Service (Paas)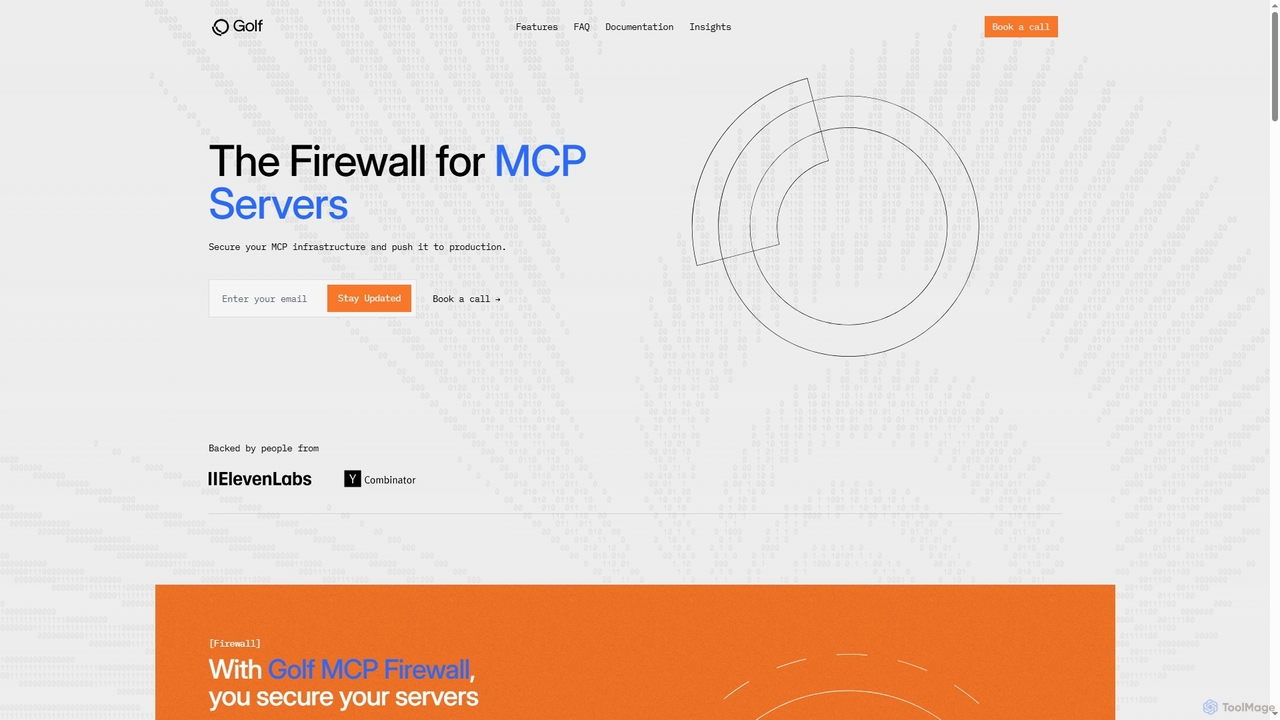
Golf
Golf is an enterprise-grade, protocol-aware firewall designed for the Model Context Protocol (MCP). It provides a centralized security layer to protect MCP servers from specific threats like prompt injection and token hijacking, enabling businesses to securely deploy AI agent infrastructure into production.
Agent Security
ZeroPath
ZeroPath is an AI-native application security (AppSec) platform that unifies SAST, SCA, secrets detection, and more. It intelligently finds and automatically fixes complex vulnerabilities, significantly reduces false positives, and seamlessly integrates into developer workflows to make security a collaborative effort.
Code Security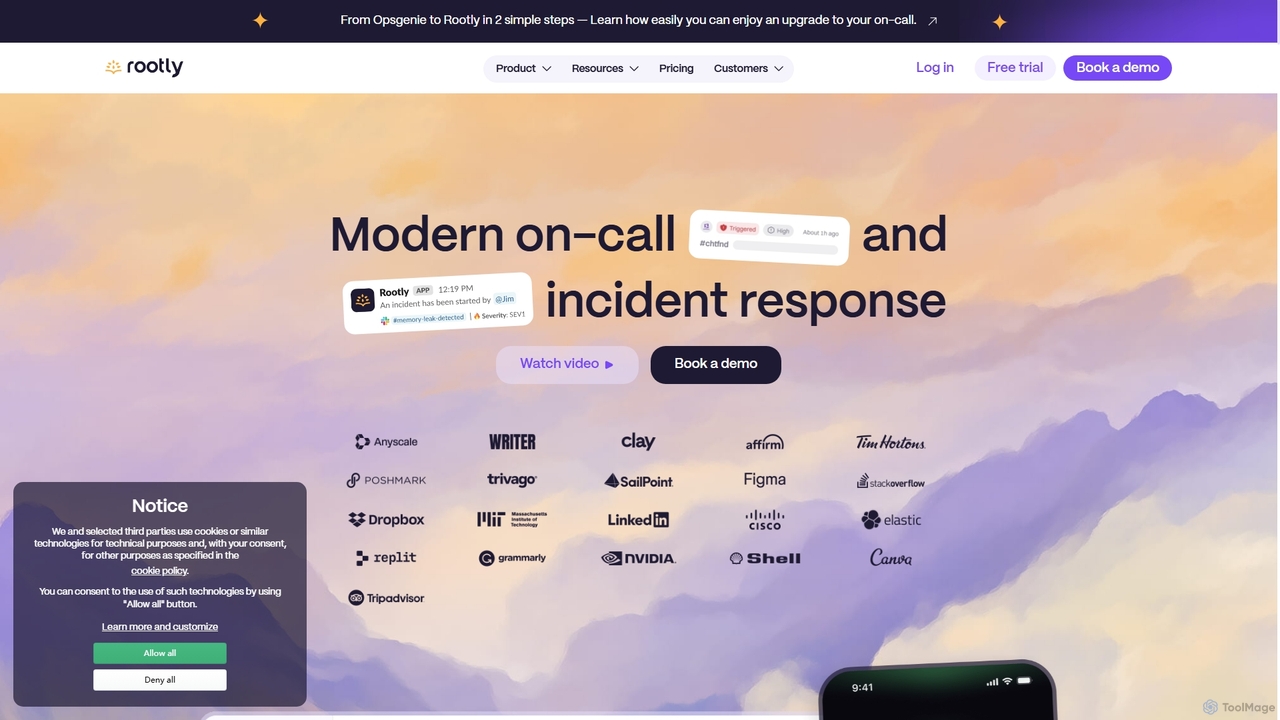
Rootly
Rootly is an AI-powered, end-to-end incident management platform designed for engineering and SRE teams. It automates the entire incident lifecycle, from on-call scheduling and alert response to resolution and post-incident analysis. By integrating seamlessly with tools like Slack, Jira, and Datadog, Rootly streamlines workflows, reduces manual tasks, and helps teams resolve issues faster, ultimately improving system reliability and operational efficiency.
Incident Management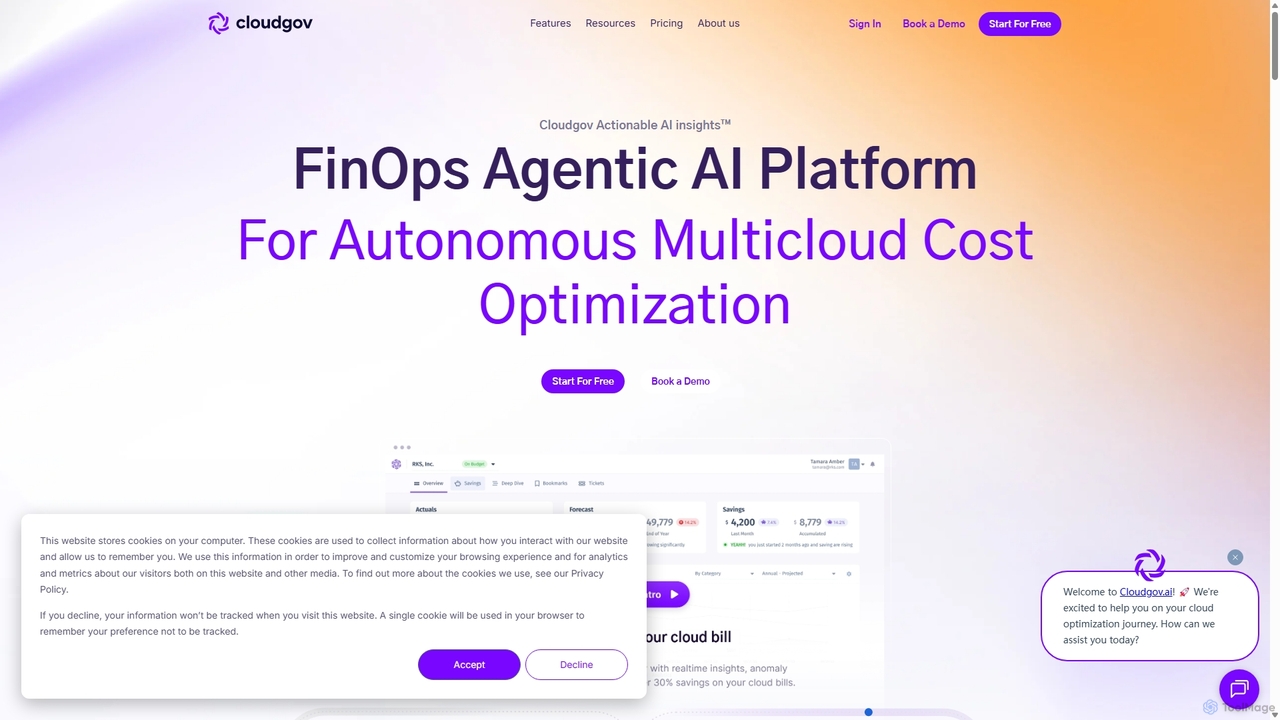
Cloudgov
Cloudgov is an agentic AI-powered FinOps platform designed for autonomous multicloud cost optimization. It provides unified visibility across AWS, Azure, and GCP, delivering actionable insights, real-time anomaly detection, and automated remediation to help businesses reduce cloud spending by over 30% and streamline financial operations.
Devops
DevOps Security Comments (0)
Sign in to comment.
Sign inNo comments yet.