

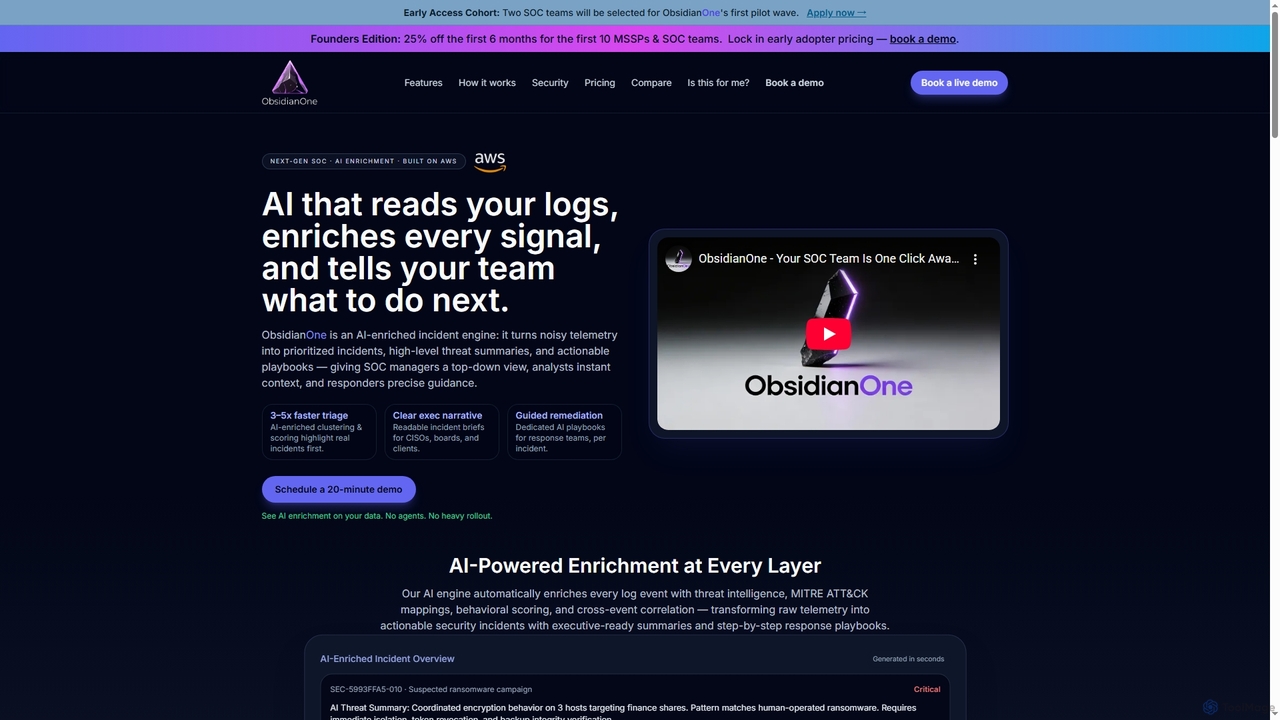
ObsidianOne Overview
ObsidianOne is an advanced AI-enriched incident engine built to revolutionize security operations for modern SOC teams and Managed Security Service Providers (MSSPs). Leveraging AWS-native AI, it intelligently reads security logs, enriches every signal with comprehensive context, and provides precise guidance for response. The platform aims to cut through alert fatigue by turning raw, noisy telemetry into actionable security incidents, complete with executive-ready summaries and step-by-step response playbooks.
How to use ObsidianOne
To use ObsidianOne, organizations first ingest their security data by connecting S3, uploading CSV/JSON files, or wiring SIEM exports. The platform automatically tags events by tenant and source. Next, ObsidianOne's AI engine enriches this data by normalizing, de-duplicating, mapping to MITRE ATT&CK, and adding threat intelligence and behavioral context. The AI then analyzes the enriched data to generate concise threat summaries, outlining what happened, why it matters, the scope, and recommended response tracks. Finally, responders utilize dedicated AI playbooks to contain, eradicate, and recover from incidents, integrating with existing ticketing and chat systems to operationalize workflows.
Core Features of ObsidianOne
- AI-Powered Incident Engine: Transforms noisy telemetry into prioritized incidents and high-level threat summaries.
- AI-Enriched Triage: Achieves 3-5x faster incident triage through intelligent clustering and scoring.
- Guided Remediation: Provides dedicated, environment-aware AI playbooks for precise response guidance.
- Comprehensive AI Enrichment: Automatically enriches log events with threat intelligence, MITRE ATT&CK mappings, behavioral scoring, and cross-event correlation.
- Executive-Ready Reporting: Generates clear, readable incident briefs for CISOs, boards, and clients.
- Native Multi-Tenant Design: Offers clean client separation and tailored playbooks for MSSPs.
- Automated Threat Intelligence: Extracts and enriches Indicators of Compromise (IOCs) from logs using global feeds like AlienVault OTX and VirusTotal.
- Continuous Learning: AI models learn from successful responses and analyst feedback to continuously improve detection and playbook effectiveness.
- AWS-Native Architecture: Ensures tenant-aware isolation, security, and compliance (SOC 2 / ISO 27001 style controls).
Use Cases for ObsidianOne
ObsidianOne is ideal for lean SOCs and MSSPs overwhelmed by alerts, seeking to enhance their incident response capabilities without massive contracts. It's used for automating alert triage, generating clear incident narratives for executives and regulators, managing multiple client environments with clean tenant separation, and operationalizing MITRE ATT&CK for real-time threat classification. The platform helps security teams move from reactive to proactive security operations, focusing on strategic threat hunting and advanced investigations while AI handles routine tasks.
Advantages of ObsidianOne
ObsidianOne offers significant advantages by reducing alert noise by up to 70%, accelerating incident triage by 3-5x, and providing instant, actionable context to security analysts. Its AI-generated playbooks ensure consistent, environment-specific remediation guidance, while automated threat intelligence enrichment eliminates manual lookup tasks. The platform's AWS-native, auditable architecture provides security and scalability without vendor lock-in or hidden costs, delivering faster time to value (hours/days) compared to traditional solutions. It empowers SOC managers with top-down views and cost insights, and enables MSSPs to scale operations efficiently across multiple clients.
Pricing and Plans
ObsidianOne offers simple, transparent volume- and tenant-based pricing, designed to be 40–70% below typical “AI SOC” add-ons from legacy vendors. They provide three main tiers: Starter, Professional, and Enterprise. The Starter plan is for small SOCs or single-team deployments, offering 1 tenant, limited log volume, AI Threat Summaries, core dashboards, MITRE ATT&CK mapping, and email support. The Professional plan, their most popular, caters to growing teams and boutique MSSPs, including multiple tenants, higher data limits, AI Summaries + AI Playbooks, multi-tenant & client management, usage & cost visibility, and priority support. The Enterprise plan is for large SOCs, MSSPs, and multi-region needs, providing all Professional features plus high-volume log intake, unlimited tenants, advanced integrations (ITSM, SIEM, chat), premium support, and optional dedicated environments. Specific pricing for all plans requires contacting ObsidianOne for a consultation or demo.
ObsidianOne FAQ
ObsidianOne Alternatives
CrowdStrike
CrowdStrike is a global cybersecurity leader with its AI-native Falcon platform. It unifies endpoint security, cloud security, identity protection, and threat intelligence into a single, lightweight agent solution. By leveraging advanced AI and real-time threat data, CrowdStrike proactively stops breaches, providing comprehensive visibility and automated protection across the entire enterprise.
It Management
BlinkOps
BlinkOps is an agentic security automation platform that empowers security teams to convert natural language prompts into powerful, no-code workflows. It enables the deployment of customized security micro-agents to automate tasks across incident response, cloud security, compliance, and more, dramatically increasing efficiency and reducing response times.
No Code
ThreatCluster
ThreatCluster is a real-time cybersecurity threat intelligence platform that aggregates, clusters, and scores threats from over 1000 sources daily, providing a focused, actionable feed without information overload.
Threat Intelligence
Cotool
Cotool is an AI security platform featuring composable agents designed for security teams. It automates alert triage, incident investigation, and threat detection, reducing manual work by up to 90%. By integrating with your existing security stack, it streamlines workflows and empowers analysts to focus on critical threats.
Devsecops
Vigilocity
Vigilocity is an AI-powered breach intelligence platform featuring "Mythic," its Offensive Impact Platform. It provides agentless, automated intelligence to confirm material security breaches by monitoring and disrupting threat actor infrastructure in real-time. Leveraging its proprietary Reverse Attack Surface Analysis (RASA), Vigilocity helps security, audit, and regulatory teams identify exfiltrated data, assess the material impact of incidents, and facilitate timely compliance with disclosure regulations.
ComplianceObsidianOne Categories
ObsidianOne Jobs
ObsidianOne Embed Widget
Copy this embed code to place the badge on your blog, article, or product site and send readers directly to this ToolMage detail page.

Related AI tools
BlinkOps
BlinkOps is an agentic security automation platform that empowers security teams to convert natural language prompts into powerful, no-code workflows. It enables the deployment of customized security micro-agents to automate tasks across incident response, cloud security, compliance, and more, dramatically increasing efficiency and reducing response times.
No Code
Protego
Protego is an advanced AI-powered cybersecurity platform offering real-time threat detection and comprehensive vulnerability assessment for enterprises. It provides continuous monitoring, lightning-fast automated scans, and deep analytics to protect digital assets and ensure compliance.
Data ProtectionCrowdStrike
CrowdStrike is a global cybersecurity leader with its AI-native Falcon platform. It unifies endpoint security, cloud security, identity protection, and threat intelligence into a single, lightweight agent solution. By leveraging advanced AI and real-time threat data, CrowdStrike proactively stops breaches, providing comprehensive visibility and automated protection across the entire enterprise.
It Management
Vectra AI
Vectra AI is an advanced cybersecurity platform that uses patented AI-driven Attack Signal Intelligence™ to detect and stop sophisticated cyberattacks across network, identity, cloud, and SaaS environments. It provides high-fidelity threat signals, reducing alert fatigue and enabling security teams to respond to real attacks up to 99% faster. Trusted by over 1,600 enterprises, Vectra AI offers unparalleled visibility and context to uncover hidden attacker behaviors that other tools miss.
Analytics
Jyek
Jyek is an AI agent platform that understands objectives, creates execution plans, uses tools, and delivers verifiable results for complex, multi-step tasks.
Automation
DSALTA
DSALTA is an AI-powered all-in-one platform that automates vendor risk, compliance, and trust management. It helps organizations achieve audit readiness in days, not months, by drafting policies, collecting evidence, assessing vendors, and fixing issues in real-time. With continuous monitoring and AI-driven remediation, DSALTA streamlines GRC workflows, reduces manual effort, and enhances security posture. A 14-day free trial is available.
Compliance Automation
mitigated.io
mitigated.io is an AI-powered risk mitigation platform that helps businesses proactively identify, analyze, and neutralize threats across cybersecurity, compliance, and operations. It leverages predictive analytics to provide actionable intelligence and automate risk management.
Compliance
Risqui
Risqui is an AI-powered platform designed to simplify and enhance information security and privacy risk management. It streamlines processes, automates risk analysis, and facilitates compliance with standards like ISO 27001. With intuitive tools for risk mapping, visualization, and team collaboration, Risqui reduces administrative overhead and improves the quality of your security strategy.
Compliance
Darkthreat
Darkthreat is an advanced AI-powered dark web monitoring platform designed to proactively detect data breaches, credential leaks, and hacker chatter before they impact your business. It provides comprehensive threat intelligence across multiple attack vectors, offering real-time alerts and data removal services to safeguard sensitive information.
Dark Web MonitoringThreatCluster
ThreatCluster is a real-time cybersecurity threat intelligence platform that aggregates, clusters, and scores threats from over 1000 sources daily, providing a focused, actionable feed without information overload.
Threat IntelligenceCotool
Cotool is an AI security platform featuring composable agents designed for security teams. It automates alert triage, incident investigation, and threat detection, reducing manual work by up to 90%. By integrating with your existing security stack, it streamlines workflows and empowers analysts to focus on critical threats.
DevsecopsVigilocity
Vigilocity is an AI-powered breach intelligence platform featuring "Mythic," its Offensive Impact Platform. It provides agentless, automated intelligence to confirm material security breaches by monitoring and disrupting threat actor infrastructure in real-time. Leveraging its proprietary Reverse Attack Surface Analysis (RASA), Vigilocity helps security, audit, and regulatory teams identify exfiltrated data, assess the material impact of incidents, and facilitate timely compliance with disclosure regulations.
Compliance
The Security Bulldog
The Security Bulldog is an AI-powered cybersecurity platform that uses a proprietary NLP engine to distill vast amounts of cyber intelligence. It helps security teams reduce manual research time, quickly identify relevant threats, make better decisions, and lower Mean Time To Remediate (MTTR).
Devsecops
greip
Greip is an AI-powered fraud prevention platform that helps online businesses detect and block fraudulent activities in real-time. It utilizes advanced techniques like device fingerprinting, behavioral analysis, and IP intelligence to provide comprehensive security, reduce chargebacks, and protect user accounts.
Analytics
Forta
Forta is a real-time threat detection and prevention network for Web3. It uses AI to monitor on-chain activity, block malicious transactions before execution, and ensure compliance. Forta secures blockchains and dApps against exploits, scams, and regulatory risks.
Blockchain
ObsidianOne Comments (0)
Sign in to comment.
Sign inNo comments yet.