
Cotool Overview
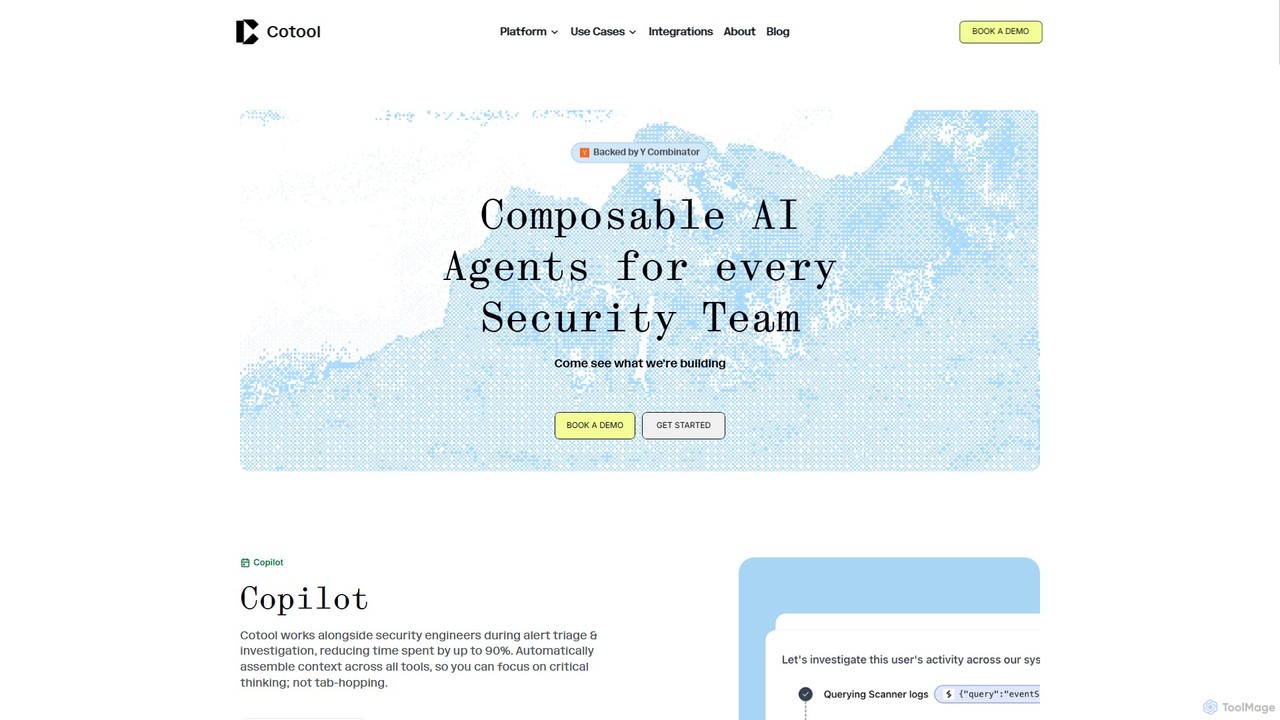
Cotool is a specialized AI security platform built to augment, not replace, security teams. Developed by experts with years of experience in top security organizations, Cotool addresses the common pain points of repetitive work and fragmented workflows. Its core mission is to empower security practitioners by automating tedious tasks, allowing them to investigate faster and concentrate on what truly matters: securing their organization. The platform works as a copilot, using composable AI agents to streamline operations across the entire security toolchain.
How to use Cotool
Using Cotool involves transforming your manual security runbooks into automated, intelligent workflows. The process typically follows these steps:
- Integration: Connect Cotool to your existing security ecosystem. This includes SIEMs, SOARs, ticketing systems (like Jira), communication platforms (like Slack), and cloud services (like AWS and Google Workspace).
- Agent Building: Build and configure AI agents for specific tasks. You can use pre-built templates or create custom agents from scratch. This process involves defining the agent's triggers, data sources, analysis logic, and actions, effectively turning your operational procedures into 'detection as code'.
- Deployment: Deploy the agents to run autonomously. They will monitor for specific events, such as a suspicious login alert or a high-severity Slack notification.
- Autonomous Execution: Once triggered, the agent automatically gathers context from all integrated tools, performs an investigation, enriches data, and documents its findings. For example, it can investigate a Jira ticket, review user behavior in Okta, and update the ticket with a summary and recommendations.
- Review and Tuning: Security teams can review the agent's work, take recommended actions, and fine-tune the agent's logic over time to improve its accuracy and efficiency, reducing false positives and adapting to new threats.
Core Features of Cotool
- Composable AI Agents: Build, customize, and deploy autonomous agents tailored to your team's specific runbooks and workflows.
- AI Copilot for Analysts: Acts as an assistant to security engineers during alert triage and investigation, automatically aggregating context from disparate tools to eliminate constant tab-hopping.
- Seamless Stack Integration: Natively integrates with a wide range of security and IT tools, including Jira, Slack, Okta, AWS, and Google Drive, creating a unified operational fabric.
- Detection as Code: Enables teams to codify their manual investigation and triage processes, creating a library of scalable, consistent, and automated agents.
- Automated Triage and Investigation: Agents can autonomously handle alerts from start to finish—from initial detection and data enrichment to ticket updates and resolution summaries.
- Proactive Threat Monitoring: Deploy agents to continuously monitor for potential threats, such as insider risks in Google Drive or misconfigurations in AWS.
Use Cases for Cotool
Cotool is versatile and can be applied across various security operations domains:
- Alert & Incident Triage: An agent can automatically investigate suspicious login alerts from Jira by checking Okta logs and user history, then post a full summary back to the ticket. Another can triage security alerts in Slack channels, reducing MTTR.
- Threat Investigation & Enrichment: When an analyst is investigating an IP address or domain, an agent can automatically run it through urlscan, query relevant logs, and summarize all related user activity across systems.
- Access & Data Security Monitoring: An agent can monitor Google Drive for excessive file sharing or suspicious access patterns to detect insider threats. Another can assist with secure employee offboarding by auditing account activity and coordinating session revocations.
- Detection Quality Improvement: An agent can investigate alerts for AWS Lambda configuration changes, determine if it's a false positive based on predefined rules, and automatically tune the detection rule, only escalating if the change is genuinely suspicious.
Advantages of Cotool
The primary advantage of Cotool is its ability to dramatically increase the efficiency and effectiveness of security teams.
- Massive Time Savings: Reduces time spent on manual triage and investigation by up to 90%.
- Enhanced Focus: Frees up security analysts from repetitive, low-value tasks to focus on complex threat hunting and strategic initiatives.
- Improved Consistency: Ensures every alert is handled with the same level of rigor and according to best practices, 24/7.
- Reduced Analyst Burnout: By automating the most tedious parts of the job, Cotool helps reduce fatigue and improve job satisfaction.
- Scalable Security Operations: Allows teams to handle a growing volume of alerts without a proportional increase in headcount.
Pricing and Plans
Cotool's pricing information is not publicly listed on their website. As a platform designed for enterprise security teams, they likely offer customized pricing plans based on the organization's size, usage volume, and specific integration needs. To get detailed pricing, interested parties should contact the Cotool sales team for a demo and a personalized quote.
Traffic
Latest traffic
Status
Monthly traffic trend
- 2025-9: 767
- 2026-1: 8.6K
- 2026-2: 23.1K
- 2026-3: 43.9K
- 2026-4: 17.4K
- 2026-5: 2.7K
Geography
Top 5 countries / regions
- 🇺🇸United States68.8%
- 🇮🇳India21.3%
- 🇯🇵Japan5.7%
- 🇦🇷Argentina4.2%
Traffic sources
| Source type | Percentage |
|---|---|
Direct | 74.7% |
Referral | 25.3% |
Top keywords
| Keyword | Cost per click |
|---|---|
| auto mode vs plan mode | $0.00 |
| context documents | $0.00 |
| cotool | $1.48 |
| cotool.ai | $0.00 |
Cotool Alternatives
BlinkOps
BlinkOps is an agentic security automation platform that empowers security teams to convert natural language prompts into powerful, no-code workflows. It enables the deployment of customized security micro-agents to automate tasks across incident response, cloud security, compliance, and more, dramatically increasing efficiency and reducing response times.
No Code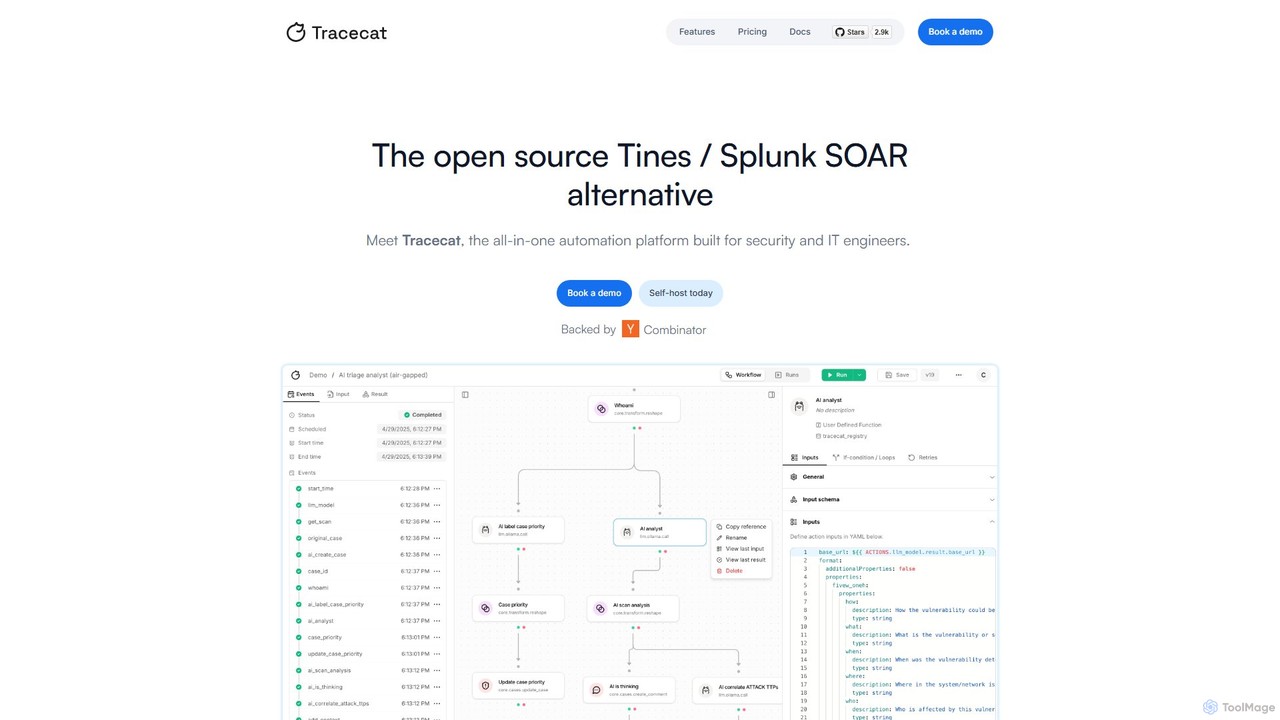
Tracecat
Tracecat is an open-source Security Orchestration, Automation, and Response (SOAR) platform designed for security and IT engineers. It serves as a powerful alternative to tools like Tines and Splunk SOAR, offering a unified solution for building automated workflows, managing cases, and utilizing lookup tables. It features a no-code visual builder alongside support for custom Python/YAML integrations, making it accessible and highly customizable.
Devops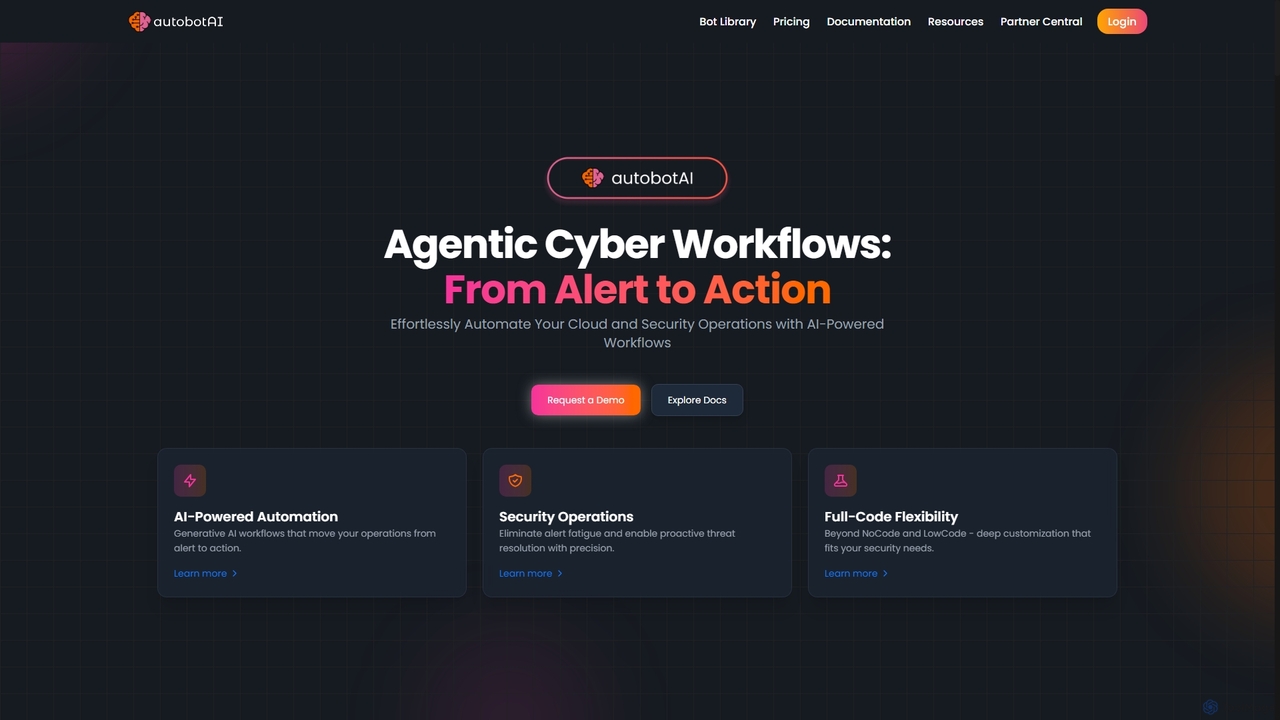
Autobot
Autobot is an AI-powered hyperautomation platform designed for cloud and security operations. It leverages generative AI and agentic workflows to transform security alerts into automated actions, significantly reducing alert fatigue and improving response times. With its full-code flexibility and universal integration capabilities, Autobot streamlines complex processes, enhances security posture, and drives operational excellence for SecOps, CloudOps, and ITOps teams.
3D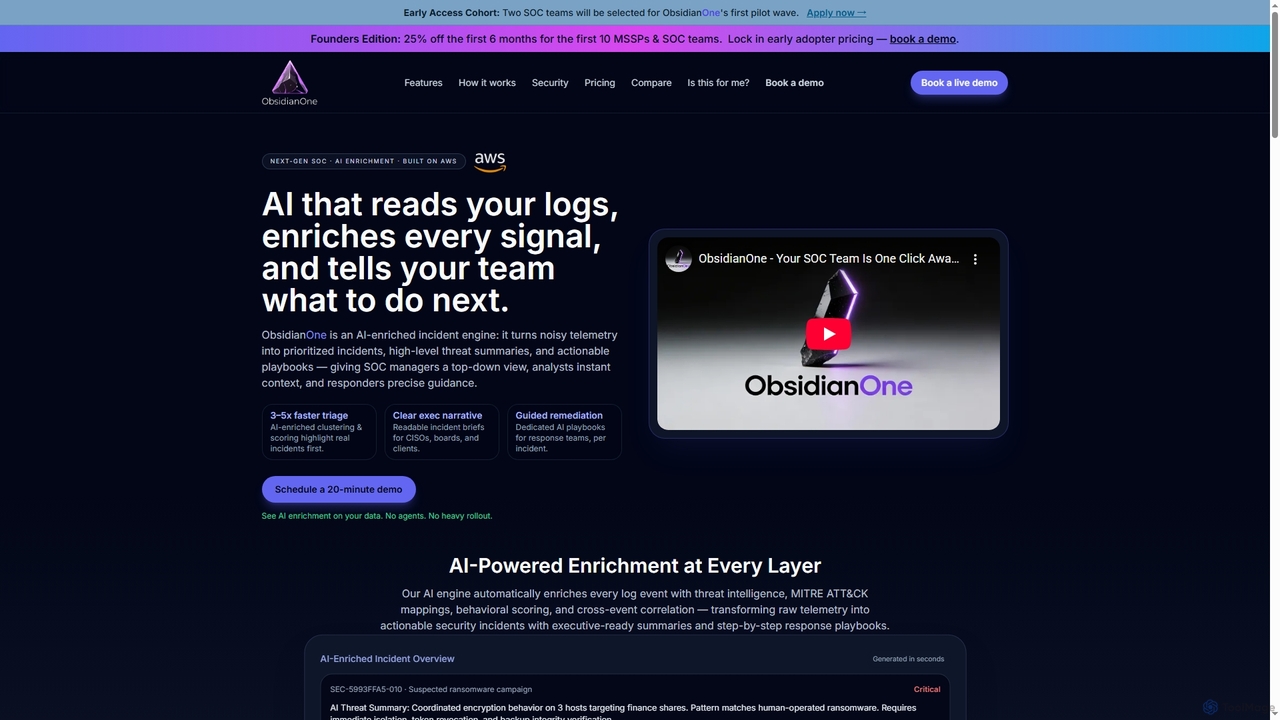
ObsidianOne
ObsidianOne is an AI-powered incident engine designed for next-generation Security Operations Centers (SOCs). It transforms noisy security telemetry into prioritized incidents, high-level threat summaries, and actionable playbooks, enabling SOC teams and MSSPs to achieve 3-5x faster triage and guided remediation.
Compliance Reporting
furl
Furl is an AI-powered autonomous remediation platform designed to help security and IT teams tackle the growing backlog of software vulnerabilities. It automates the entire remediation lifecycle, from consolidating vulnerability data and prioritizing risks to generating and deploying tailored fixes. By replacing manual processes with intelligent automation, Furl doubles productivity and secures enterprise systems efficiently.
DevsecopsCotool Categories
Cotool Embed Widget
Copy this embed code to place the badge on your blog, article, or product site and send readers directly to this ToolMage detail page.

Related AI tools
BlinkOps
BlinkOps is an agentic security automation platform that empowers security teams to convert natural language prompts into powerful, no-code workflows. It enables the deployment of customized security micro-agents to automate tasks across incident response, cloud security, compliance, and more, dramatically increasing efficiency and reducing response times.
No CodeTracecat
Tracecat is an open-source Security Orchestration, Automation, and Response (SOAR) platform designed for security and IT engineers. It serves as a powerful alternative to tools like Tines and Splunk SOAR, offering a unified solution for building automated workflows, managing cases, and utilizing lookup tables. It features a no-code visual builder alongside support for custom Python/YAML integrations, making it accessible and highly customizable.
DevopsAutobot
Autobot is an AI-powered hyperautomation platform designed for cloud and security operations. It leverages generative AI and agentic workflows to transform security alerts into automated actions, significantly reducing alert fatigue and improving response times. With its full-code flexibility and universal integration capabilities, Autobot streamlines complex processes, enhances security posture, and drives operational excellence for SecOps, CloudOps, and ITOps teams.
3DObsidianOne
ObsidianOne is an AI-powered incident engine designed for next-generation Security Operations Centers (SOCs). It transforms noisy security telemetry into prioritized incidents, high-level threat summaries, and actionable playbooks, enabling SOC teams and MSSPs to achieve 3-5x faster triage and guided remediation.
Compliance Reporting
Jyek
Jyek is an AI agent platform that understands objectives, creates execution plans, uses tools, and delivers verifiable results for complex, multi-step tasks.
Automation
Vectra AI
Vectra AI is an advanced cybersecurity platform that uses patented AI-driven Attack Signal Intelligence™ to detect and stop sophisticated cyberattacks across network, identity, cloud, and SaaS environments. It provides high-fidelity threat signals, reducing alert fatigue and enabling security teams to respond to real attacks up to 99% faster. Trusted by over 1,600 enterprises, Vectra AI offers unparalleled visibility and context to uncover hidden attacker behaviors that other tools miss.
Analytics
Chatwhitehat
Chatwhitehat is an AI-powered assistant designed for ethical hackers and cybersecurity professionals. It revolutionizes security workflows by providing intelligent, real-time strategies for both offensive (Red Team) and defensive (Blue Team) operations. Leverage its vast knowledge base to master skills, build robust security plans, and get personalized solutions for any cybersecurity challenge, from vulnerability analysis to incident response.
Code Assistant
win3zz
win3zz is an AI-powered cybersecurity platform designed for proactive threat detection and vulnerability management. It automates penetration testing, scans for vulnerabilities across web, mobile, and network assets, and provides AI-driven code analysis to help developers and security teams build and maintain secure applications.
Code Analysisfurl
Furl is an AI-powered autonomous remediation platform designed to help security and IT teams tackle the growing backlog of software vulnerabilities. It automates the entire remediation lifecycle, from consolidating vulnerability data and prioritizing risks to generating and deploying tailored fixes. By replacing manual processes with intelligent automation, Furl doubles productivity and secures enterprise systems efficiently.
Devsecops
Veriom
Veriom is an autonomous AI security platform that acts as a neural layer for your infrastructure, SaaS, and AI systems. It goes beyond detection by mapping, prioritizing, and automatically fixing cybersecurity and compliance risks in real-time. By eliminating alert fatigue and manual triage, Veriom provides continuous assurance and proactive risk management.
Devsecops
codegate
Codegate is an open-source security gateway and multiplexing framework for AI agentic systems. Developed by Stacklok, it provides secure workspaces and policy-based access control, enabling developers to build and manage complex multi-agent applications safely and efficiently.
Agentic Frameworks
Akto
Akto is an AI-powered, agentic API security platform for modern application security teams. It automates the entire API security lifecycle, from discovery and inventory to testing and runtime protection. Using autonomous AI agents, Akto continuously monitors, tests, and secures APIs, identifying vulnerabilities, sensitive data exposure, and business logic flaws 50x faster than manual methods.
Api Security
ethiack
Ethiack is an autonomous ethical hacking platform that combines AI-powered automated penetration testing with elite human hackers. It provides continuous 24/7 security testing to identify and prioritize vulnerabilities across your entire digital infrastructure, helping you stay compliant and secure before threats are exploited.
Testing
StrongestLayer
StrongestLayer is an AI-driven email security platform that specializes in detecting and neutralizing advanced phishing attacks, including those crafted by generative AI. It provides real-time threat analysis and an 'Inbox Advisor' to empower users, closing the security gaps left by traditional defense systems and protecting organizations from zero-day threats and business email compromise.
Risk Management
Casco
Casco is an autonomous security testing platform for AI systems. It acts as a continuous, always-on AI red team, proactively identifying and helping to fix vulnerabilities in AI agents, applications, and infrastructure before malicious attackers can exploit them, replacing periodic penetration testing with year-round automated monitoring.
Model Security
Cotool Comments (0)
Sign in to comment.
Sign inNo comments yet.