
Niyantri Security Overview
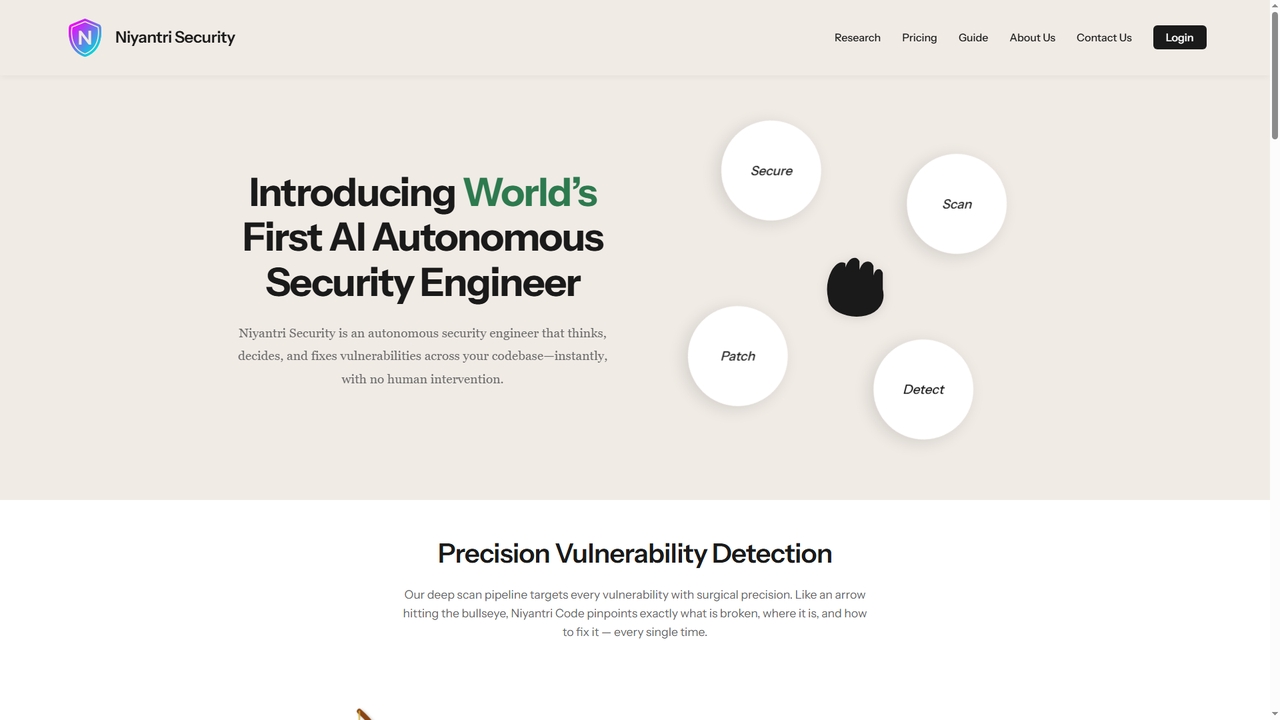
Niyantri Security is an advanced AI tool that acts as an autonomous security engineer, specializing in proactive code vulnerability management. It moves beyond simple detection by understanding code architecture, tracing cross-file data flows, and providing precise, automated fixes with minimal human intervention. The system is built to integrate directly into the software development lifecycle, offering both deep analysis and actionable remediation.
How to use Niyantri Security
Using Niyantri Security involves a straightforward three-step process. First, connect your code repository by authorizing the native GitHub App for read-only access to your chosen repository and branch, or by directly uploading a ZIP archive of your project. Second, initiate a deep AI scan which automatically maps your code architecture, hunts for vulnerabilities with full context (CVSS, CWE, severity), and generates a structured report. Third, review the findings and apply fixes with one click to generate a patched file or open a GitHub Pull Request with the corrections pre-applied.
Core Features of Niyantri Security
- Four-Phase Deep Scan Pipeline: AI-driven analysis that summarizes files, builds a global architectural model, categorizes risk domains, and surfaces vulnerabilities with context (CVSS scores, CWE IDs, cross-file impact chains).
- Context-Aware & Cross-File Analysis: Detects vulnerabilities by understanding function-level blast radius, taint source tracking, and inter-file data flows, not just surface-level syntax.
- Autonomous Surgical Auto-Fix: One-click generation of patched files or GitHub PRs that modify only the vulnerable lines of code, verified for syntax correctness.
- GitHub & File Upload Integration: Native GitHub App integration for repository scanning or direct ZIP upload without needing a repository.
- Comprehensive Reporting & Visualization: Generates detailed reports with Critical/High/Medium/Low/Info severity levels and offers 3D visualization of findings.
- Multi-Language Support: Supports scanning for vulnerabilities in over 15 programming languages including JavaScript, TypeScript, Python, Go, Java, PHP, Ruby, Rust, and C/C++.
Use Cases for Niyantri Security
Niyantri Security is ideal for development teams seeking to shift security left in their SDLC. It is used for pre-commit security checks, continuous integration pipeline security gates, auditing legacy codebases for hidden vulnerabilities, and automatically generating security patches for identified issues. It helps organizations enforce security guardrails and maintain a fortified codebase against emerging threats.
Advantages of Niyantri Security
Niyantri Security offers significant advantages over traditional SAST tools. Its deep, context-aware analysis reduces false positives and identifies complex, cross-file vulnerabilities that other tools miss. The autonomous, surgical fix capability dramatically reduces remediation time and effort. The platform requires no manual rule creation or maintenance, learns from code patterns, and integrates seamlessly into existing developer workflows through GitHub.
Niyantri Security FAQ
Niyantri Security Alternatives
CipherClaw
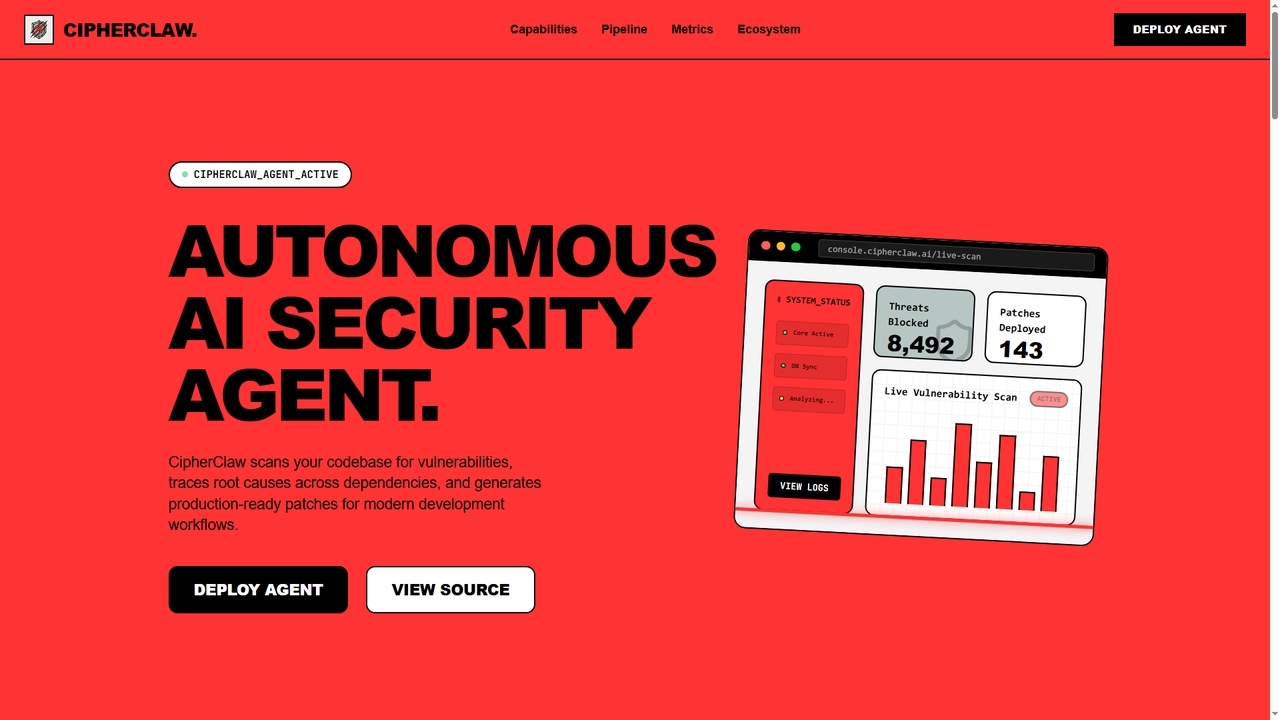
CipherClaw is an autonomous AI security agent that proactively scans your codebase for vulnerabilities, performs root cause analysis across dependencies using advanced causal graph and abstract geometric analysis, and autonomously generates and deploys production-ready patches. Designed for modern, AI-generated development workflows, it integrates seamlessly with ecosystems like OpenClaw, NVIDIA Nemo Claw, Lovable, and n8n.
Code Generation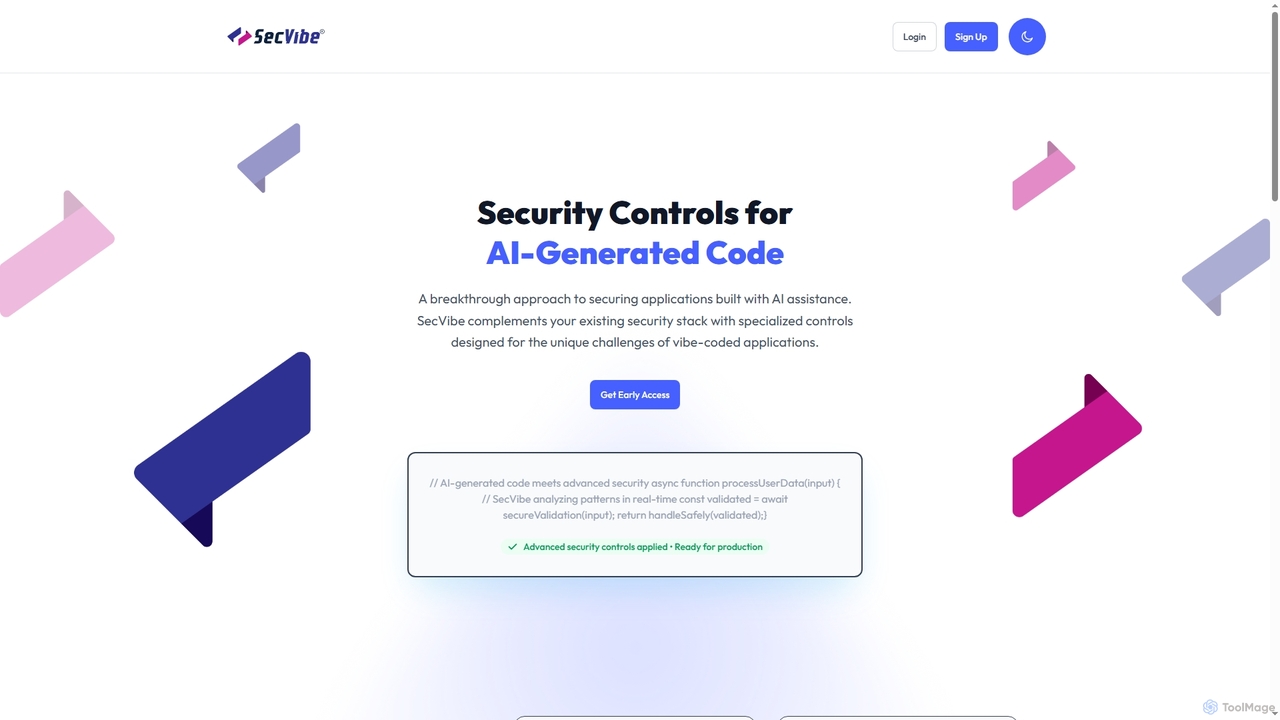
SecVibe
SecVibe is a cutting-edge security platform designed to protect applications built with AI-generated code. It offers specialized controls, real-time analysis, and context-aware mechanisms to identify and mitigate unique security vulnerabilities often missed by traditional tools. SecVibe seamlessly integrates with existing security stacks, enhancing overall application security for modern, AI-assisted development workflows without compromising speed.
Code Analysis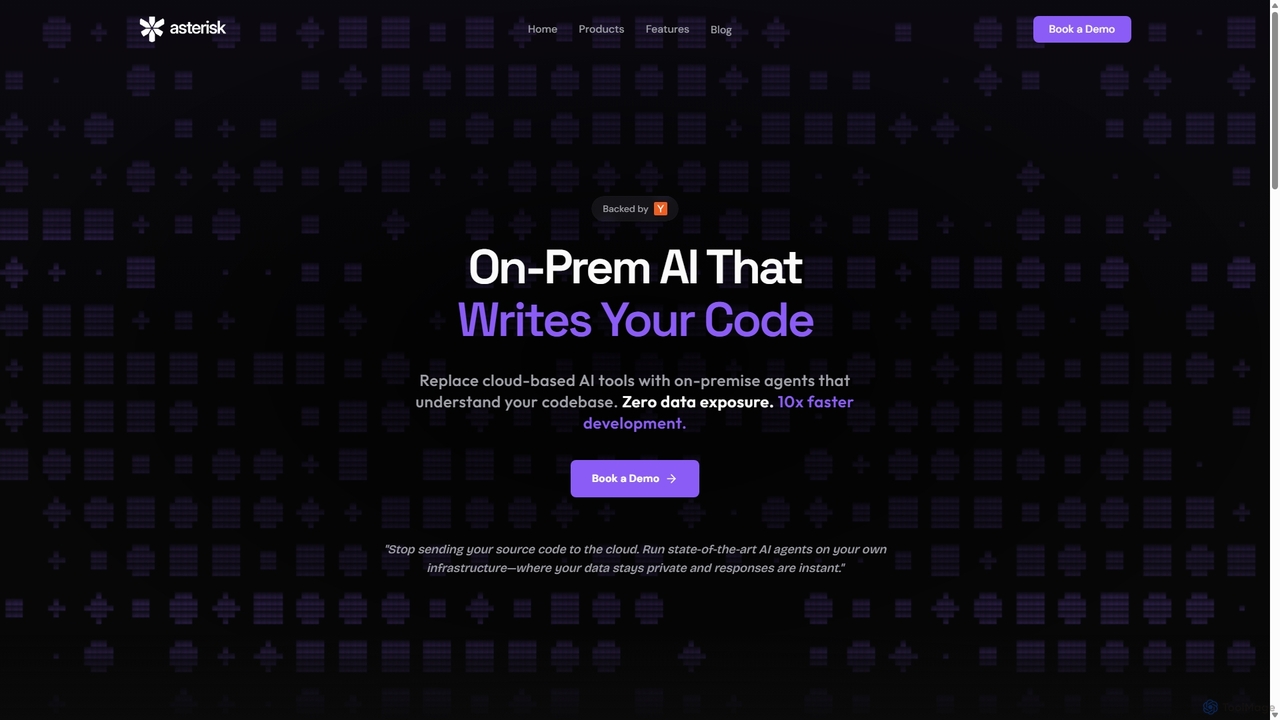
Asterisk
Asterisk is an on-premise AI code intelligence platform designed for enterprises. It offers a suite of secure AI agents for autonomous coding, advanced security scanning, and codebase Q&A, ensuring zero data exposure, lightning-fast performance, and full control over your infrastructure. It's built for privacy-conscious development at scale.
Code Assistant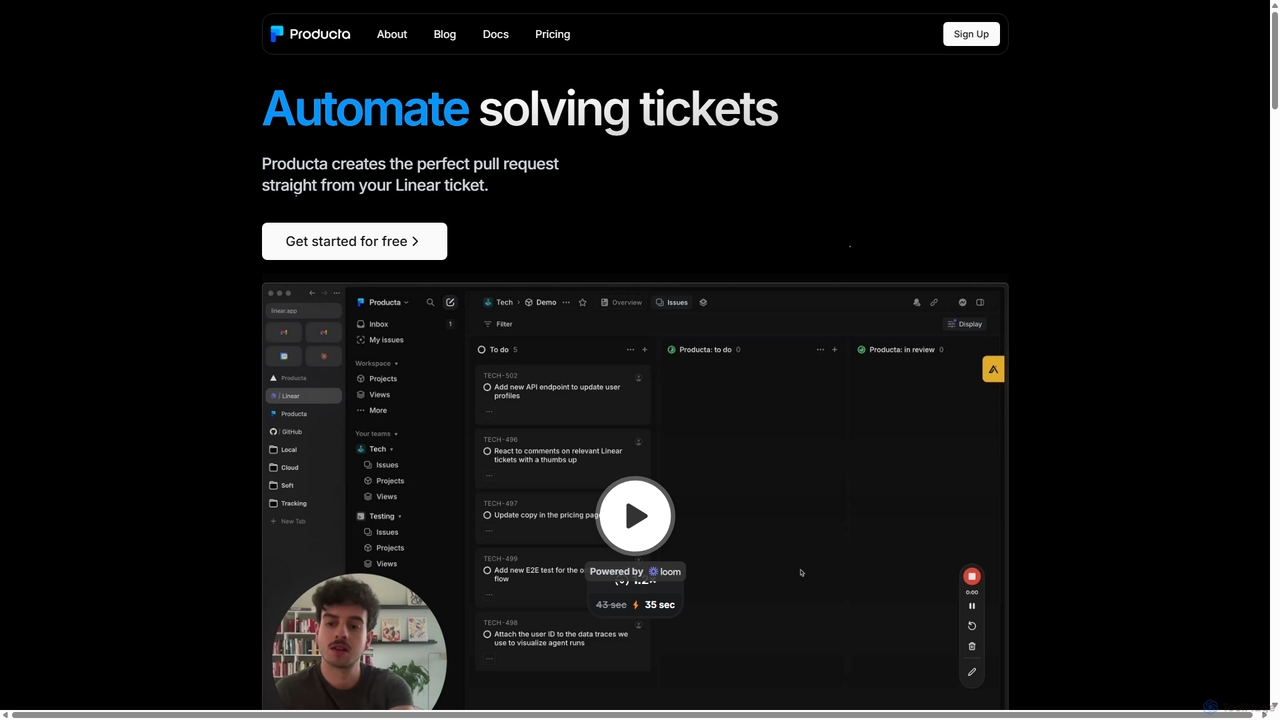
Producta
Producta is an AI-powered software development assistant that automates the entire workflow from a Linear ticket to a GitHub pull request. It intelligently clarifies tasks, generates, tests, and refines code, integrating seamlessly into your existing development process to accelerate bug fixes and feature implementation.
Automation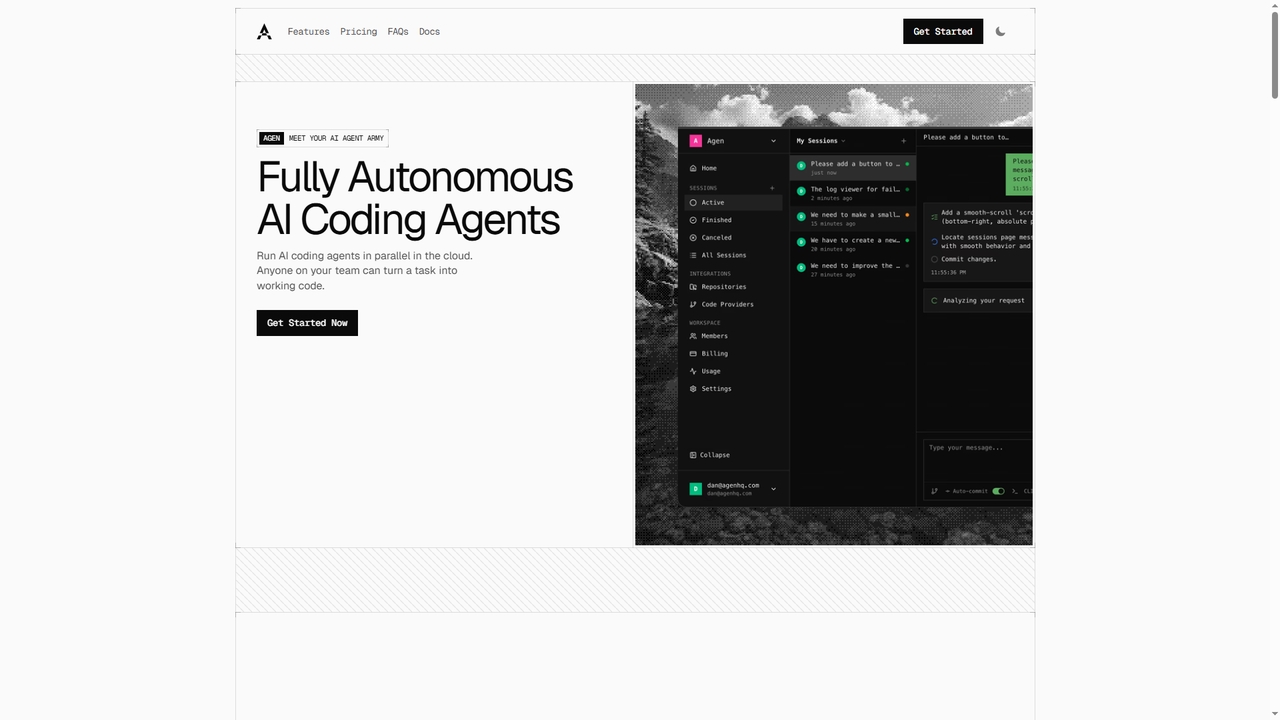
Agen
Agen is a cloud-based platform that deploys fully autonomous AI coding agents. It enables developers and teams to assign software development tasks via prompts. The agents independently clone repositories, analyze codebases, edit files, run builds and tests in isolated sandboxes, and prepare merge requests, streamlining the development workflow from idea to production-ready code.
AutomationNiyantri Security Categories
Niyantri Security Jobs
Niyantri Security Embed Widget
Copy this embed code to place the badge on your blog, article, or product site and send readers directly to this ToolMage detail page.

Related AI tools
SecVibe
SecVibe is a cutting-edge security platform designed to protect applications built with AI-generated code. It offers specialized controls, real-time analysis, and context-aware mechanisms to identify and mitigate unique security vulnerabilities often missed by traditional tools. SecVibe seamlessly integrates with existing security stacks, enhancing overall application security for modern, AI-assisted development workflows without compromising speed.
Code AnalysisCipherClaw
CipherClaw is an autonomous AI security agent that proactively scans your codebase for vulnerabilities, performs root cause analysis across dependencies using advanced causal graph and abstract geometric analysis, and autonomously generates and deploys production-ready patches. Designed for modern, AI-generated development workflows, it integrates seamlessly with ecosystems like OpenClaw, NVIDIA Nemo Claw, Lovable, and n8n.
Code GenerationAsterisk
Asterisk is an on-premise AI code intelligence platform designed for enterprises. It offers a suite of secure AI agents for autonomous coding, advanced security scanning, and codebase Q&A, ensuring zero data exposure, lightning-fast performance, and full control over your infrastructure. It's built for privacy-conscious development at scale.
Code Assistant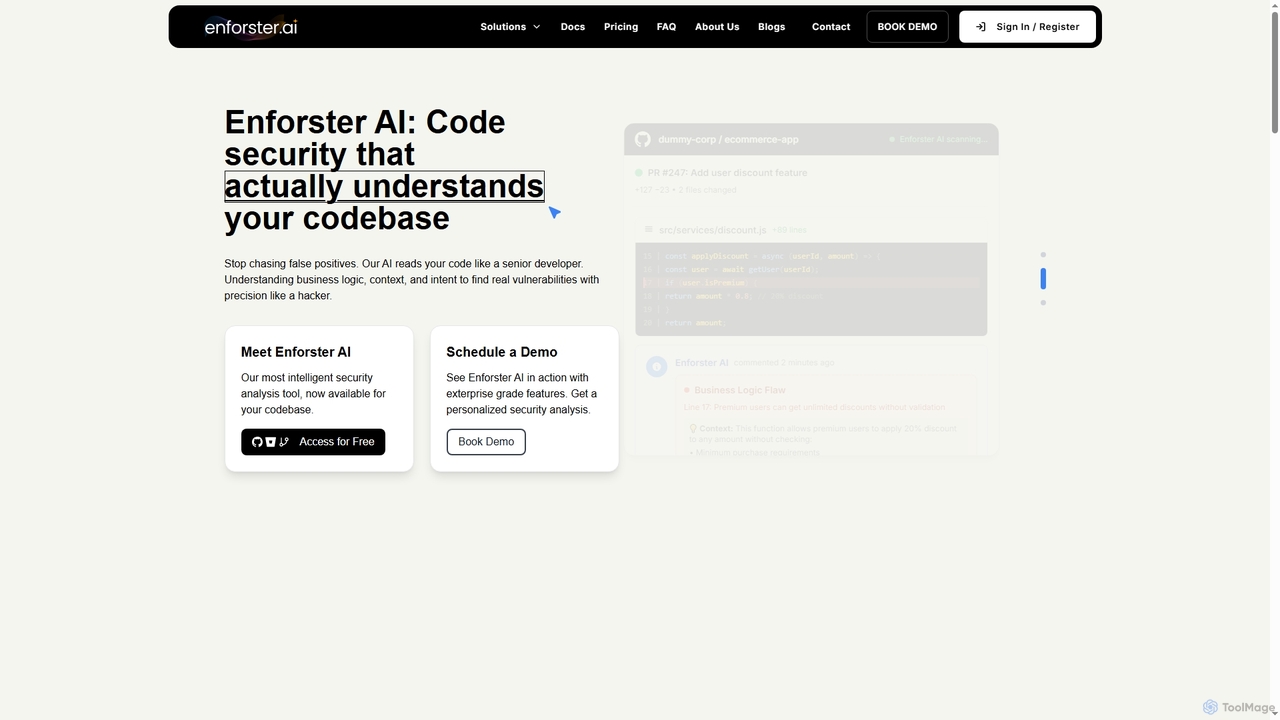
Enforster AI
Enforster AI is an AI-native Static Application Security Testing (SAST) tool that analyzes code like a senior developer. It understands business logic and context to identify real vulnerabilities with 90% accuracy, reducing false positives by 60% and providing AI-generated fixes.
Code Analysis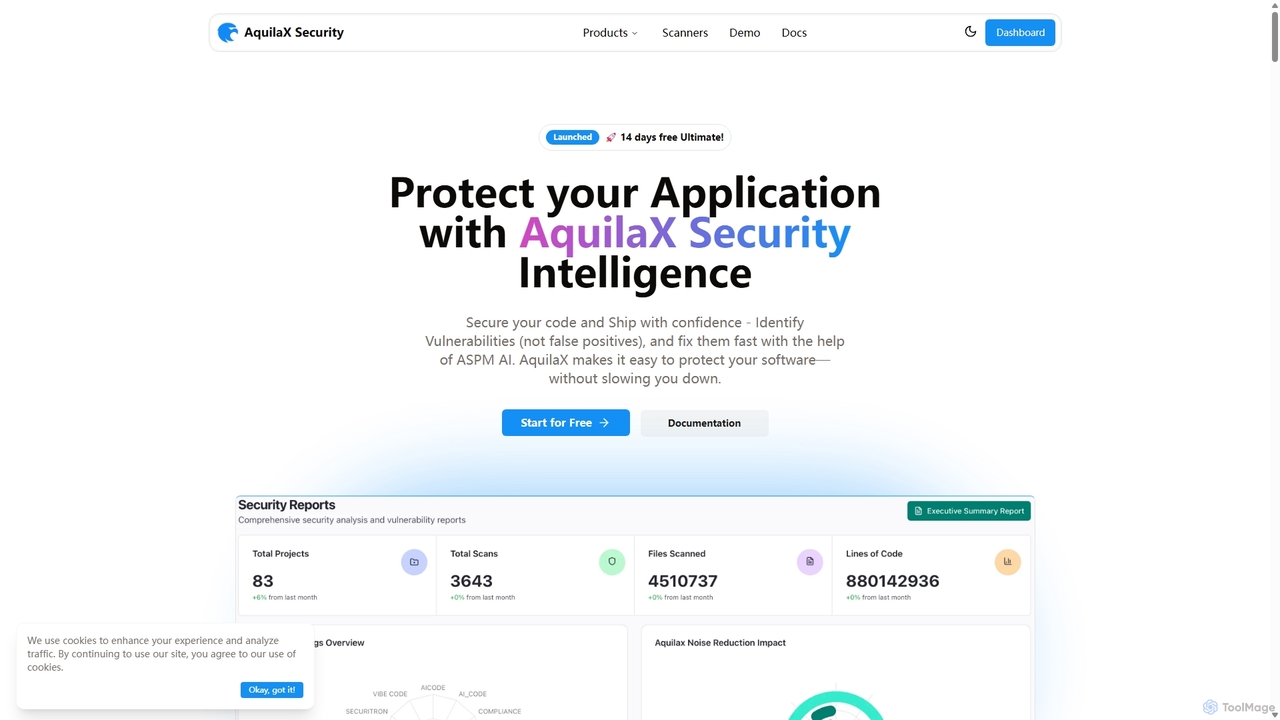
Aquilax
AquilaX is an AI-powered DevSecOps platform designed to secure software throughout the development lifecycle. It integrates seamlessly into CI/CD pipelines, offering a suite of 12 advanced scanners for vulnerabilities, secrets, and compliance. With its self-learning AI model, AquilaX dramatically reduces false positives, provides actionable remediation steps, and empowers teams to ship secure code with confidence and speed.
Code Security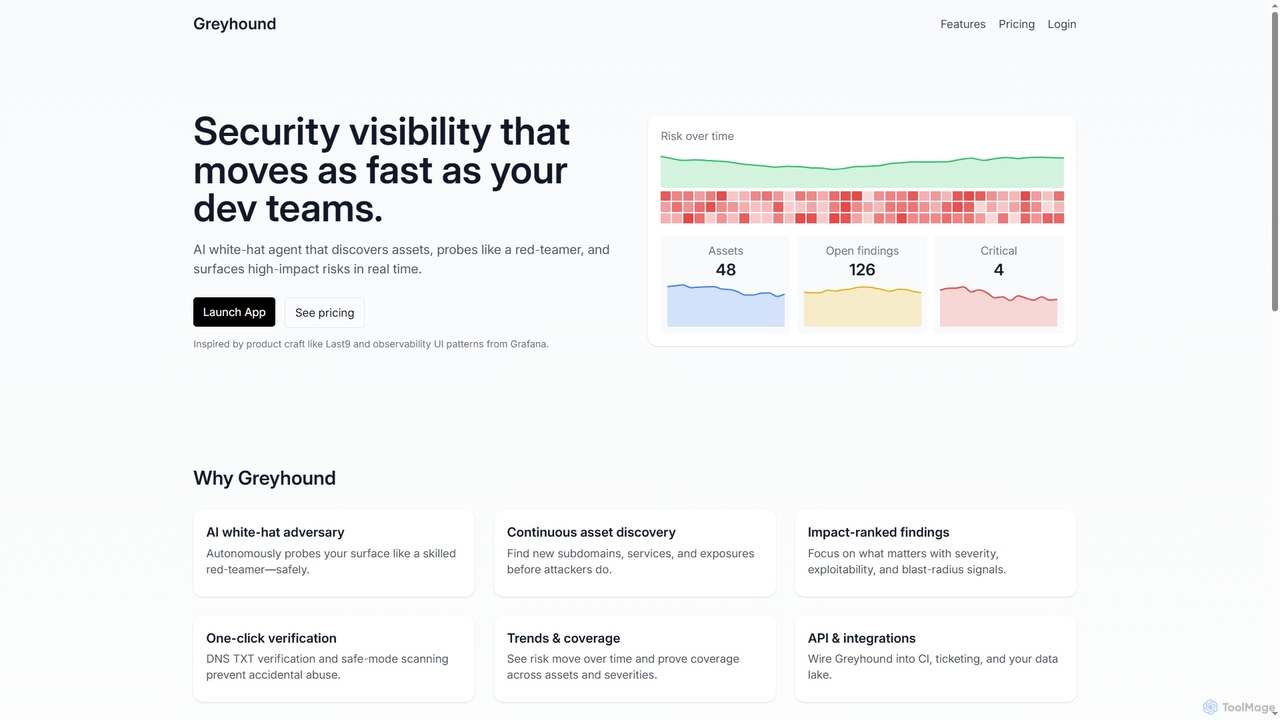
Greyhound
Greyhound is an AI-powered security platform that provides continuous scanning for web and cloud assets. It emulates a skilled attacker to autonomously discover assets, identify vulnerabilities, and provide impact-ranked findings with clear remediation steps, helping teams focus on critical risks.
Cloud Security
AppSanctuary
AppSanctuary is an AI-powered application security platform that automates vulnerability scanning, compliance checks, and threat detection. It helps developers and security teams build and maintain secure mobile and web applications by providing deep code analysis, actionable remediation advice, and seamless CI/CD integration.
Security & Compliance
win3zz
win3zz is an AI-powered cybersecurity platform designed for proactive threat detection and vulnerability management. It automates penetration testing, scans for vulnerabilities across web, mobile, and network assets, and provides AI-driven code analysis to help developers and security teams build and maintain secure applications.
Code Analysis
Jyek
Jyek is an AI agent platform that understands objectives, creates execution plans, uses tools, and delivers verifiable results for complex, multi-step tasks.
Automation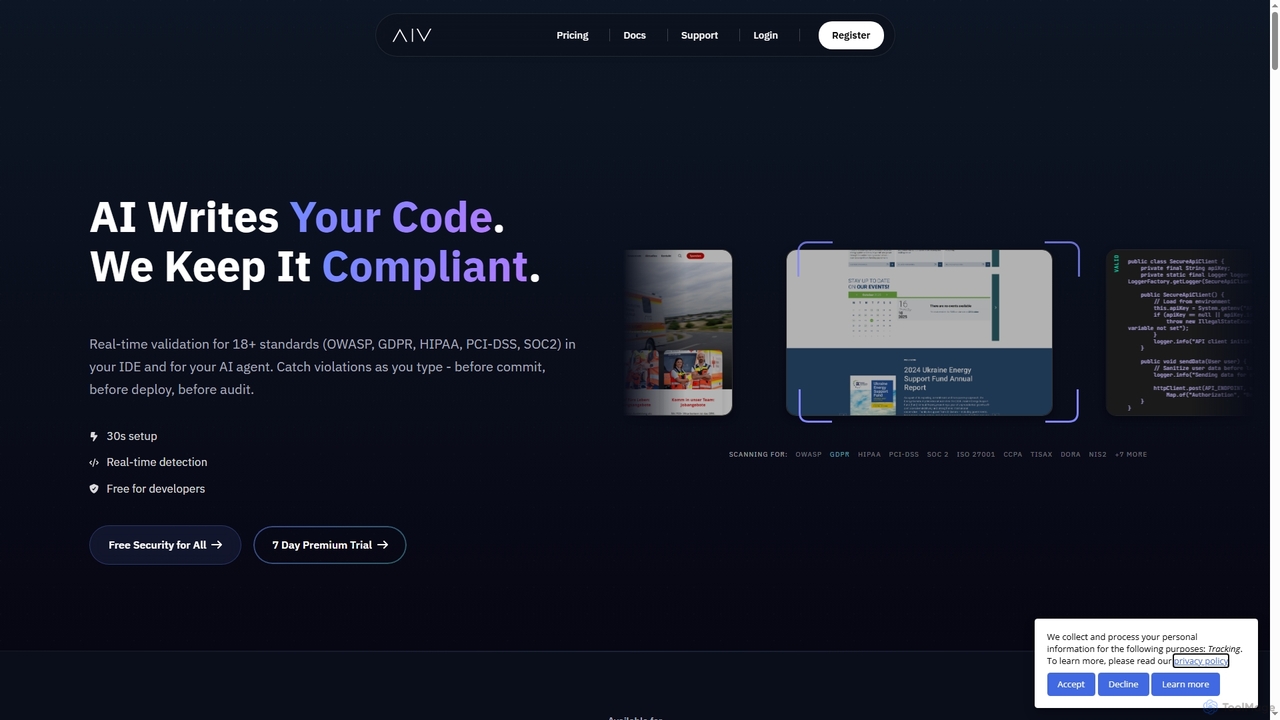
Aivory
Aivory is a real-time compliance and security validation tool for developers. It integrates into IDEs like VS Code and JetBrains to scan AI-generated and human-written code as you type, catching violations against 18+ standards (GDPR, HIPAA, OWASP) before they are committed, saving significant time and cost.
Code Quality
Crowdbotics
Crowdbotics is an AI-powered platform that transforms software development by analyzing codebases to extract deep insights. It automatically generates architectural diagrams, business requirements, and file-level analysis, helping engineering teams understand complex systems, reduce technical debt, and accelerate development cycles. Ideal for modernizing legacy code and onboarding new developers.
Code Analysis
GenieEngage
GenieEngage is a DevOps-as-a-Service partner providing expert solutions in DevOps, DevSecOps, and GitOps. It helps businesses accelerate software delivery, enhance security, and scale infrastructure on clouds like AWS, Azure, and GCP, offering a full team of experts as a cost-effective alternative to in-house hiring.
Infrastructure Management
Zerothreat
ZeroThreat is an AI-powered continuous penetration testing and DAST platform designed to secure web applications and APIs. It automates the detection of over 40,000 vulnerabilities, including OWASP Top 10 and CVEs, providing fast, accurate, and actionable security insights for developers and security teams.
Testing
Code Wiki
Code Wiki is an AI-powered documentation hub by Google, built on Gemini models. It automatically analyzes code repositories to generate up-to-date documentation, interactive architectural diagrams, and a conversational chat interface, helping developers understand complex codebases faster.
Code Analysis
Kerno
Kerno is an AI-powered co-pilot for backend developers, autonomously generating, running, and maintaining exhaustive integration test suites. It understands your code, dependencies, and business logic to deliver reliable, high-quality testing at scale, directly within your IDE.
Backend Development
Niyantri Security Comments (0)
Sign in to comment.
Sign inNo comments yet.