

CipherClaw Overview
CipherClaw is an active, autonomous AI security agent designed for modern software development environments. It moves beyond traditional static analysis by leveraging deep code understanding and abstract geometric analysis to identify zero-day vulnerabilities and complex security threats within your entire codebase and its dependency chain. The system autonomously traces the root cause of issues and generates ready-to-deploy patches, creating a continuous and intelligent security remediation pipeline.
How to use CipherClaw
Using CipherClaw involves a streamlined, autonomous pipeline. First, connect your code repository to the CipherClaw agent via its OpenClaw GitHub integration tools. Once connected, the AI vulnerability scanner immediately begins a deep, abstract geometric analysis of your codebase. The system then autonomously performs root cause tracing across dependencies and, upon detecting vulnerabilities, proceeds to generate and deploy production-ready AI code patches automatically, completing the remediation cycle without manual intervention.
Core Features of CipherClaw
- Autonomous AI Security Agent: An active system that continuously scans, analyzes, and remediates code vulnerabilities.
- Causal Graph Code Analysis: AI-powered root cause analysis that traces vulnerabilities with extreme precision across the entire dependency chain, eliminating manual tracing of spaghetti code.
- AI Brain Fingerprints for Code: Creates unique vulnerability signatures for intelligent pattern recognition, enabling threat neutralization at scale.
- Predictive Vulnerability Scanning: Uses predictive behavioral analysis and AI software supply chain security to catch zero-day vulnerabilities before they surface.
- Threat Memory Tier Architecture: Features a structured bug classification hierarchy, multi-level threat memory for persistent tracking, and predictive “Crystal Ball” analysis.
- Autonomous Code Remediation: Automatically generates and deploys production-ready patches, forming a complete security pipeline.
Use Cases for CipherClaw
CipherClaw is essential for development teams seeking to automate and enhance their security posture. It is particularly valuable for securing AI-generated codebases from platforms like Lovable, integrating security into n8n automation workflows, and providing enterprise-grade vulnerability management within the OpenClaw and NVIDIA Nemo Claw ecosystems. It replaces manual triage and outdated static analysis tools for modern development workflows.
Advantages of CipherClaw
CipherClaw offers several key advantages: It automates the entire vulnerability detection-to-patch cycle, saving countless hours of manual work. Its deep, causal analysis provides precise root cause identification, unlike superficial static scanners. The predictive scanning capability offers proactive protection against zero-day threats. Finally, its native integrations with popular modern development ecosystems (OpenClaw, Lovable, n8n, NVIDIA) ensure seamless deployment and operation within existing workflows.
CipherClaw FAQ
CipherClaw Alternatives
Niyantri Security
Niyantri Security is an AI-powered autonomous security engineer designed to automatically detect and fix vulnerabilities in your codebase. It performs deep, multi-phase scans to identify security flaws with context, provides surgical auto-fixes, and seamlessly integrates into development workflows via GitHub or direct file upload.
Automation
furl
Furl is an AI-powered autonomous remediation platform designed to help security and IT teams tackle the growing backlog of software vulnerabilities. It automates the entire remediation lifecycle, from consolidating vulnerability data and prioritizing risks to generating and deploying tailored fixes. By replacing manual processes with intelligent automation, Furl doubles productivity and secures enterprise systems efficiently.
Devsecops
Repodex
Repodex is an AI-powered code intelligence platform that helps developers and teams search, understand, and manage their code repositories. Using natural language, you can find code, get explanations, and generate documentation instantly.
Code Generation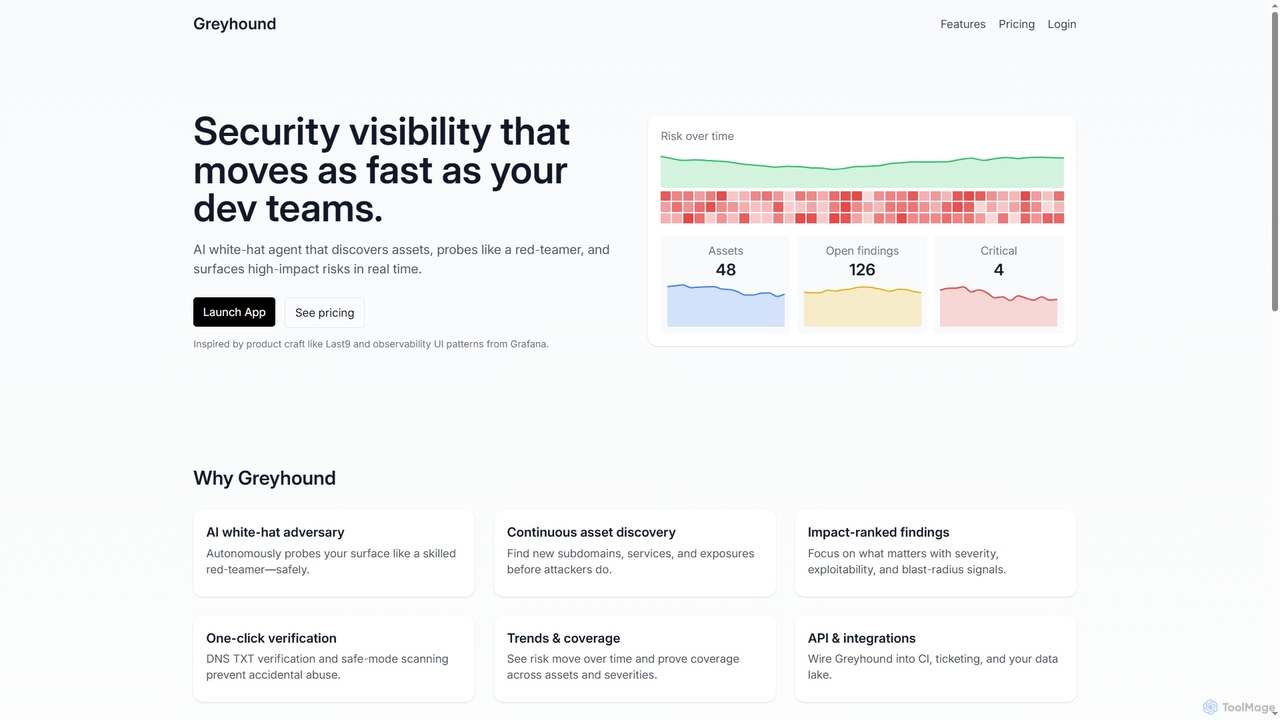
Greyhound
Greyhound is an AI-powered security platform that provides continuous scanning for web and cloud assets. It emulates a skilled attacker to autonomously discover assets, identify vulnerabilities, and provide impact-ranked findings with clear remediation steps, helping teams focus on critical risks.
Cloud Security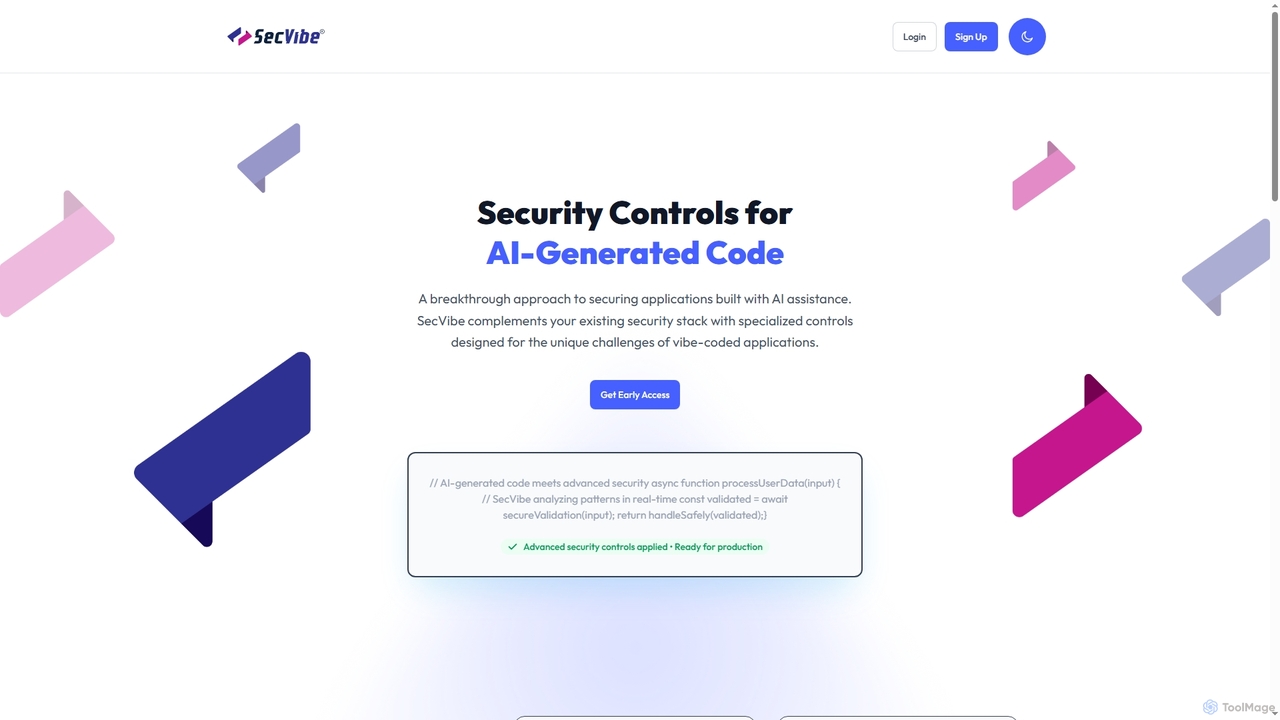
SecVibe
SecVibe is a cutting-edge security platform designed to protect applications built with AI-generated code. It offers specialized controls, real-time analysis, and context-aware mechanisms to identify and mitigate unique security vulnerabilities often missed by traditional tools. SecVibe seamlessly integrates with existing security stacks, enhancing overall application security for modern, AI-assisted development workflows without compromising speed.
Code AnalysisCipherClaw Categories
CipherClaw Jobs
CipherClaw Embed Widget
Copy this embed code to place the badge on your blog, article, or product site and send readers directly to this ToolMage detail page.

Related AI tools
Niyantri Security
Niyantri Security is an AI-powered autonomous security engineer designed to automatically detect and fix vulnerabilities in your codebase. It performs deep, multi-phase scans to identify security flaws with context, provides surgical auto-fixes, and seamlessly integrates into development workflows via GitHub or direct file upload.
AutomationGreyhound
Greyhound is an AI-powered security platform that provides continuous scanning for web and cloud assets. It emulates a skilled attacker to autonomously discover assets, identify vulnerabilities, and provide impact-ranked findings with clear remediation steps, helping teams focus on critical risks.
Cloud SecuritySecVibe
SecVibe is a cutting-edge security platform designed to protect applications built with AI-generated code. It offers specialized controls, real-time analysis, and context-aware mechanisms to identify and mitigate unique security vulnerabilities often missed by traditional tools. SecVibe seamlessly integrates with existing security stacks, enhancing overall application security for modern, AI-assisted development workflows without compromising speed.
Code Analysis
Aquilax
AquilaX is an AI-powered DevSecOps platform designed to secure software throughout the development lifecycle. It integrates seamlessly into CI/CD pipelines, offering a suite of 12 advanced scanners for vulnerabilities, secrets, and compliance. With its self-learning AI model, AquilaX dramatically reduces false positives, provides actionable remediation steps, and empowers teams to ship secure code with confidence and speed.
Code Security
AppSanctuary
AppSanctuary is an AI-powered application security platform that automates vulnerability scanning, compliance checks, and threat detection. It helps developers and security teams build and maintain secure mobile and web applications by providing deep code analysis, actionable remediation advice, and seamless CI/CD integration.
Security & Compliance
win3zz
win3zz is an AI-powered cybersecurity platform designed for proactive threat detection and vulnerability management. It automates penetration testing, scans for vulnerabilities across web, mobile, and network assets, and provides AI-driven code analysis to help developers and security teams build and maintain secure applications.
Code Analysis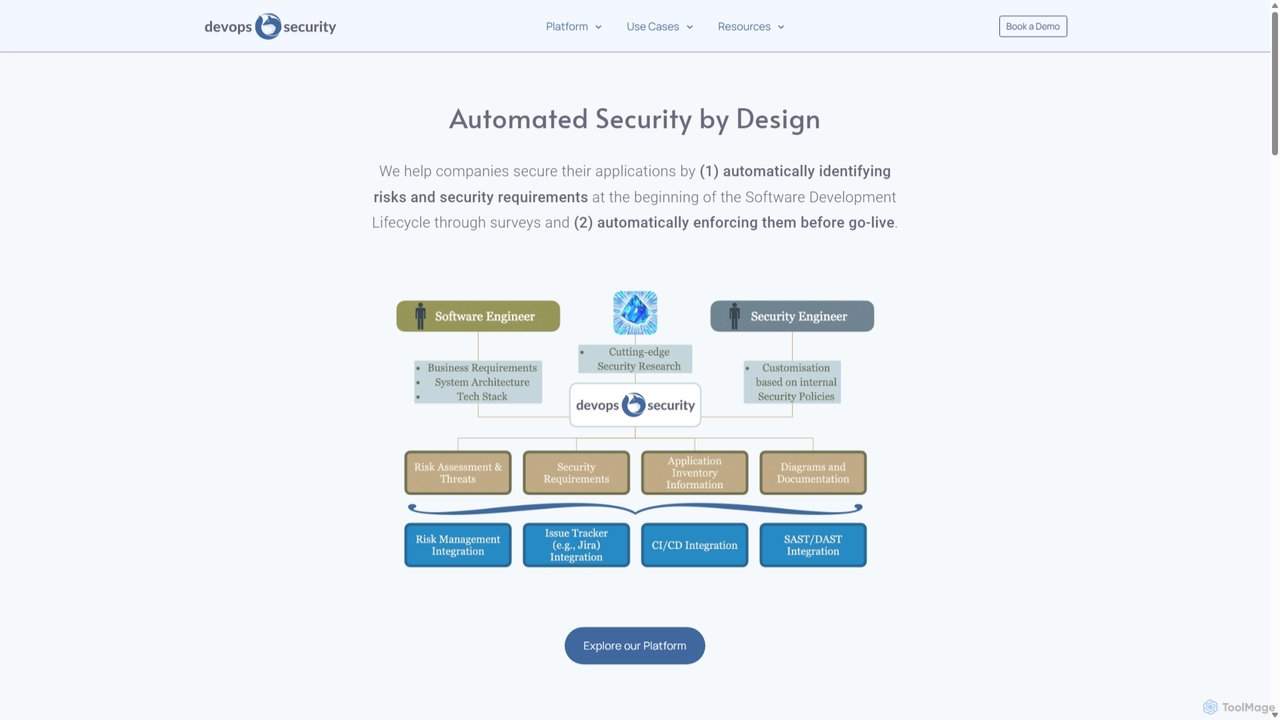
DevOps Security
An AI-native platform that automates application security by integrating risk assessment and requirement enforcement directly into the Software Development Lifecycle (SDLC). It helps companies shift security left, empowering developers and streamlining security processes from design to deployment.
Security
Jyek
Jyek is an AI agent platform that understands objectives, creates execution plans, uses tools, and delivers verifiable results for complex, multi-step tasks.
Automation
Zerothreat
ZeroThreat is an AI-powered continuous penetration testing and DAST platform designed to secure web applications and APIs. It automates the detection of over 40,000 vulnerabilities, including OWASP Top 10 and CVEs, providing fast, accurate, and actionable security insights for developers and security teams.
Testingfurl
Furl is an AI-powered autonomous remediation platform designed to help security and IT teams tackle the growing backlog of software vulnerabilities. It automates the entire remediation lifecycle, from consolidating vulnerability data and prioritizing risks to generating and deploying tailored fixes. By replacing manual processes with intelligent automation, Furl doubles productivity and secures enterprise systems efficiently.
Devsecops
Enforster AI
Enforster AI is an AI-native Static Application Security Testing (SAST) tool that analyzes code like a senior developer. It understands business logic and context to identify real vulnerabilities with 90% accuracy, reducing false positives by 60% and providing AI-generated fixes.
Code Analysis
Asterisk
Asterisk is an on-premise AI code intelligence platform designed for enterprises. It offers a suite of secure AI agents for autonomous coding, advanced security scanning, and codebase Q&A, ensuring zero data exposure, lightning-fast performance, and full control over your infrastructure. It's built for privacy-conscious development at scale.
Code Assistant
GenieEngage
GenieEngage is a DevOps-as-a-Service partner providing expert solutions in DevOps, DevSecOps, and GitOps. It helps businesses accelerate software delivery, enhance security, and scale infrastructure on clouds like AWS, Azure, and GCP, offering a full team of experts as a cost-effective alternative to in-house hiring.
Infrastructure Management
Snyk
Snyk is an AI-powered developer security platform that helps businesses build software securely. It proactively finds and fixes vulnerabilities in custom code, open-source dependencies, containers, and Infrastructure as Code (IaC) throughout the entire development lifecycle, from IDE to production.
Code Security
ethiack
Ethiack is an autonomous ethical hacking platform that combines AI-powered automated penetration testing with elite human hackers. It provides continuous 24/7 security testing to identify and prioritize vulnerabilities across your entire digital infrastructure, helping you stay compliant and secure before threats are exploited.
Testing
CipherClaw Comments (0)
Sign in to comment.
Sign inNo comments yet.